⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More
Some attacks this week didn’t need much of a trick. A fake support call, a trusted extension, a shared link, or a device with no
Some attacks this week didn’t need much of a trick. A fake support call, a trusted extension, a shared link, or a device with no
A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led
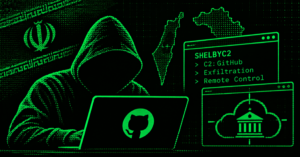
Cybersecurity researchers have disclosed details of a cyber espionage campaign targeting Israel and the Kurdistan Region of Iraq by an Iran state-aligned threat actor between
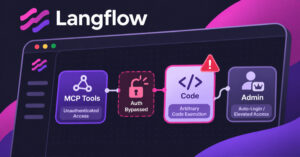
Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week. Langflow is an
Forty percent of security teams now use AI every day, and another 56% are testing it. Only 4% have no plans to adopt it, according
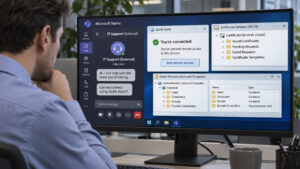
Attackers posing as IT support on Microsoft Teams talked employees into giving them remote control of their PCs. They then used insecure Active Directory Certificate