India Mandates Registered Caller Name Display on 4G and Newer Networks From November 1

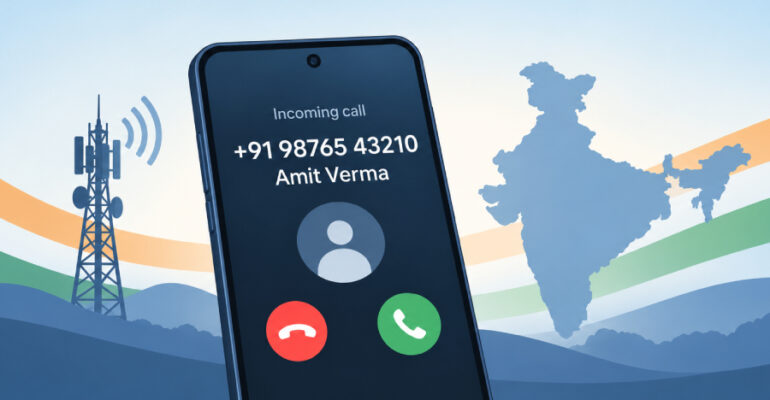
The Indian government has directed telecom service providers (TSPs) in the country to mandatorily display callers’ registered names along with their numbers for incoming calls starting November 1, 2026, in an effort to help people identify calls from unknown numbers
GhostAction Compromises About 1,900 GitHub Accounts, Targets Over 30,000 Repositories

The credential-theft campaign known as GhostAction has ramped up, targeting more than 30,000 repositories across 3,000 users and organizations. The spike, according to GitGuardian, was observed on October 8 and 9, 2026. “This resulted from compromising the GitHub accounts of

Langflow’s Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts

Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian. Langflow is an open-source platform that allows developers to build artificial intelligence (AI) applications and agentic workflows. In February 2025, DataStax, the parent company

AhsayCBS Flaws Exploited to Deploy Web Shells Get New Fixes After Incomplete Patches

Singapore-based Ahsay Backup has released security updates to address two security flaws in AhsayCBS that have been exploited by bad actors to drop web shells and XMRig cryptocurrency miners. The vulnerabilities in question are CVE-2026-105133 and CVE-2026-105134, which could be

Palo Alto Networks Patches PAN-OS Authenticated RCE Flaw Amid Active Exploitation

Palo Alto Networks on Wednesday issued security updates for a high-severity flaw in PAN-OS software that has come under active exploitation. The vulnerability, tracked as CVE-2026-0322 (CVSS score: 8.6), is a case of remote code execution in the management interface.