Russian Police Arrest 3 Suspected VasyGrek Hackers, Dismantle Criminal Infrastructure

Russian authorities have arrested three suspected members of a threat group known as VasyGrek and dismantled its criminal infrastructure. Also known as Fluffy Wolf, the threat actor has a history of targeting Russian and international companies since 2016. The Ministry
Google Issues Patches for Critical Android Flaw That Could Allow RCE Without User Interaction

A critical Android flaw could allow an attacker to run code on a phone without any user action remotely, Google said in its November security bulletin. The flaw, CVE-2026-58868, affects Android 14 through 17. Phones get the fix with security patch

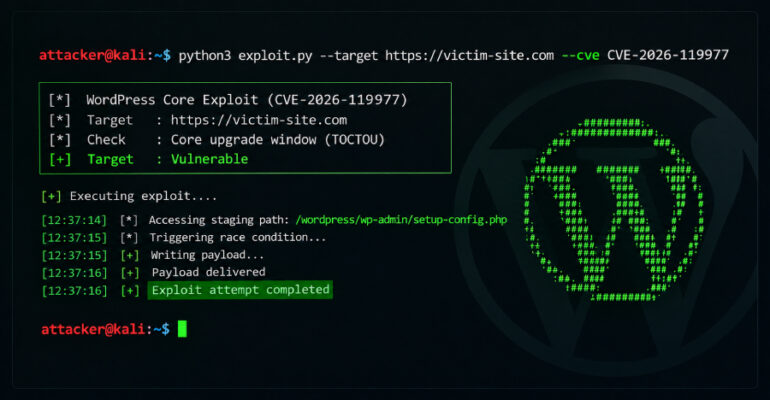
CISA Confirms Hackers Exploiting WordPress Core Flaw During Software Upgrades

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The high-severity vulnerability, tracked as CVE-2026-119977 (CVSS score: 8.1), is a case

mSecure Warns Users to Change Passwords, Reset 2FA and Passkeys After Suspicious Activity

Customers of the mSecure password manager are being urged to act now to protect the confidential information they store in it, possibly by changing passwords, resetting two-factor authentication (2FA), and removing passkeys. The warning came in an email sent on

Chainstack Reports Production Systems Breach Exposing Customer Data and Password Hashes

Blockchain infrastructure provider Chainstack on Tuesday disclosed that it was targeted in a cyber attack that allowed an unauthorized party to gain access to some parts of its infrastructure. The incident is assessed to be part of a large-scale, artificial

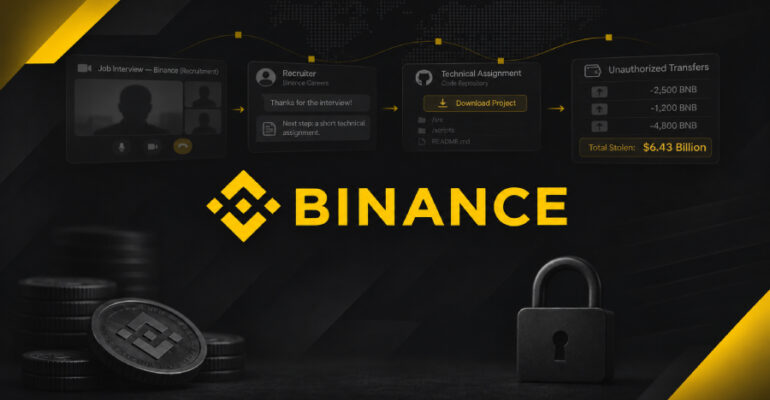
Binance Reveals How Fake Job Interviews and AI Tool Abuse Led to $6.43 Billion Theft

Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world’s largest cryptocurrency exchange was the culmination of a “sophisticated, multi-stage campaign” that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack

Barracuda Flaws Could Be Chained to Bypass Authorization and Gain Root Access

Barracuda has disclosed details of two vulnerabilities affecting its products that, if chained together, could allow an attacker to bypass authorization controls and gain root access to a susceptible device. The vulnerabilities, a pre-authentication authorization bypass vulnerability and a command

Google Warns LLMjacking Attacks Are Costing Some Enterprises Up to $1 Million in Cloud Charges

Google on Monday warned that threat actors are hijacking enterprise access to Large Language Models (LLMs) to fraudulently leverage expensive computing resources and AI services. The tactic is called LLMjacking, a form of resource hijacking adapted for the LLM era,

cPGuard Update Channel Hijacked to Backdoor Linux Servers and Collect Password Hashes

An attacker broke into the update system of the cPGuard security tool on November 2 and used it to send a malicious script to customers’ Linux servers. The script installed a backdoor and collected password hashes and other sensitive files

Red Hat Patches 9.8-Rated Linux TCP RCE Flaw While Ubuntu Releases Fixes for Testing

Fixed kernels for a use-after-free vulnerability in the Linux kernel’s IPv4 TCP code are now available for Red Hat Enterprise Linux 8, 9, and 10, while Ubuntu’s fixes for its three newest long-term-support releases remain in its opt-in testing channel with no