New Zapscape KVM Flaw Could Let Privileged L1 Guest Code Escape to Linux Hosts

Zapscape, a new Linux kernel vulnerability, could allow an attacker with kernel privileges inside an L1 guest virtual machine (VM) to escape KVM isolation and execute code on the host. The risk applies when nested virtualization is exposed to untrusted
Cisco Patches 12 SD-WAN and IOS XE Flaws, Including Three 9.8 CVSS Score Bugs

Cisco has rolled out updates to address multiple critical security vulnerabilities impacting Catalyst SD-WAN and IOS XE Software as part of a comprehensive internal security review. The security issues affect Cisco Catalyst SD-WAN Software, regardless of device configuration, and Cisco

New Interrupt Injection Attack Can Bypass Spectre v2 Defenses on Intel and AMD CPUs

An unprivileged Linux program can time a hardware interrupt to land in the gap between a processor sanitizing its branch predictor and the kernel using it, re-poisoning the predictor after the defense has run. MIT CSAIL researchers Daniël Trujillo and

ThreatsDay: Odysseus RCE, Samsung One-Click Takeover, iCloud Backdoor Fight + 27 More Stories

Apparently, opening the thing is now enough. A repo can run before the first prompt, a package can hide among hundreds, and a harmless-looking PDF can finish the job. This week runs on cheap leverage: exposed servers, recycled bugs, poisoned

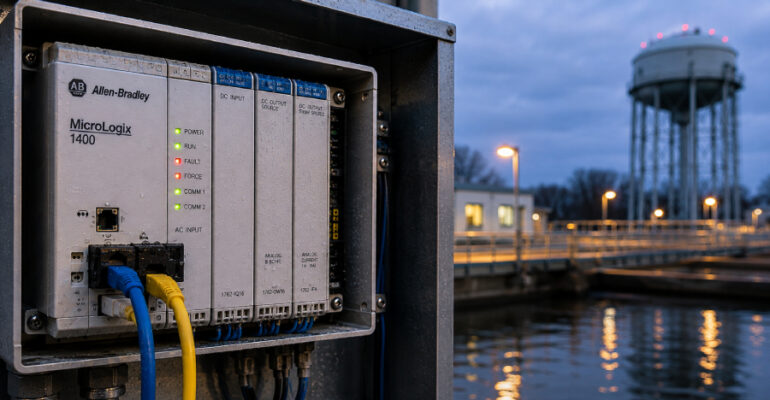
Over 4,400 Rockwell PLCs Exposed Online, 22 Found in Water Attack Cities

Forescout found 22 internet-facing Rockwell Automation programmable logic controllers (PLCs) in cities hit by recent cyberattacks on US water utilities. Nineteen used the same mobile carrier network. Its August 3 scan counted 4,407 exposed Rockwell controllers worldwide, including 2,844 in

CryptoJS Weak RNG Behind $5.7 Million in Drains Affects Five Crypto Wallet Apps

Coinspect has identified CryptoJS.lib.WordArray.random() as the weak random number generator behind the Ill Bloom wallet drains. Introduced in the JavaScript cryptography library 12 years ago, the function supplied weak entropy that affected wallet apps used to generate recovery phrases. Coinspect’s

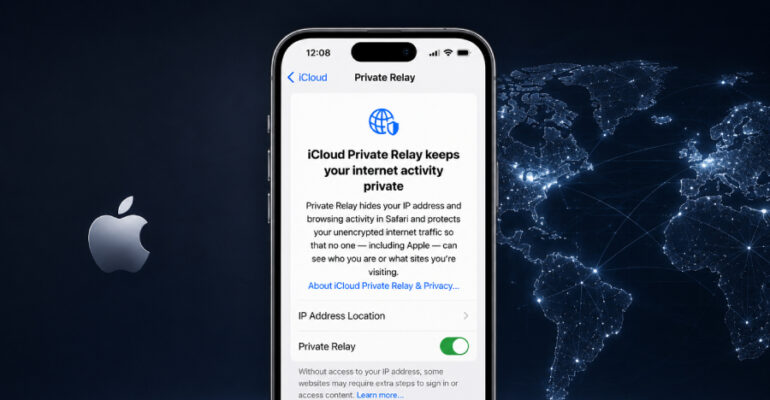
Apple iCloud Private Relay Can Expose Real IPs Through WebKit Proxy Bypasses

Cybersecurity researchers have disclosed a security issue with Apple’s iCloud Private Relay tool that can expose a user’s real IP address. Introduced with iOS 15, iCloud Private Relay employs a dual-hop architecture to ensure users’ privacy by routing their Safari

AI Recommendation Poisoning: How “Ask AI” Buttons Silently Alter LLM Memory

A new class of prompt injection is spreading across commercial websites. It requires no malware, no stolen credentials, and no zero-day exploit. It abuses a standard feature built into almost every major AI assistant: pre-filled deep links. We observed production

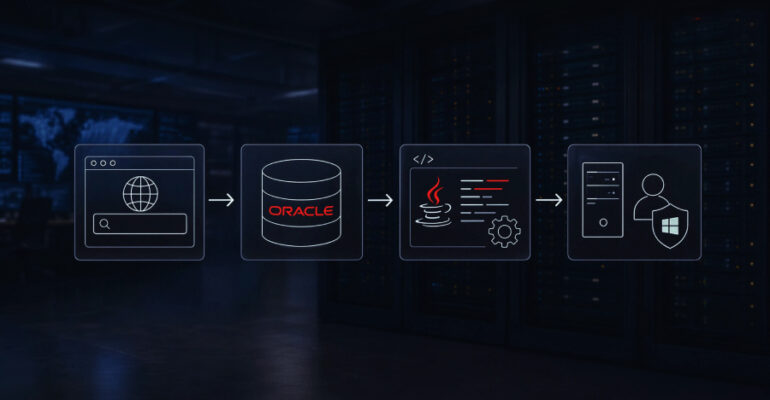
Attackers Compile khunt Inside Oracle to Turn SQL Injection Into Windows SYSTEM Access

Attackers broke into an organization’s Oracle database through a SQL injection flaw in a public-facing web application, then installed a post-exploitation toolkit without writing an executable to disk. They fed Java source code to the database, let Oracle compile it

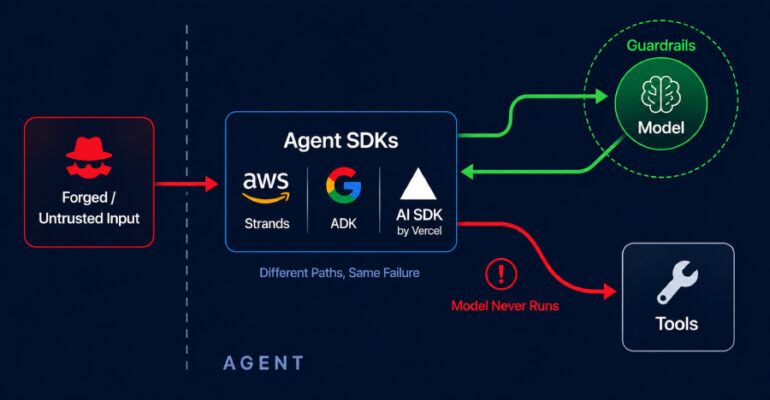
AWS, Google, and Vercel Agent Flaws Let Attackers Trigger Tools Without Running the Model

Security flaws in agent infrastructure from Amazon Web Services (AWS), Google, and Vercel let untrusted or forged instructions reach an agent’s tools with no check that a model turn had authorized them. In several of the attack paths, the model