Nearly 800 Malicious npm Packages Deliver Cross-Platform RAT and Infostealer

A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targeting Windows, Mac, and Linux systems. “These packages appear to use AI slop squatted, or
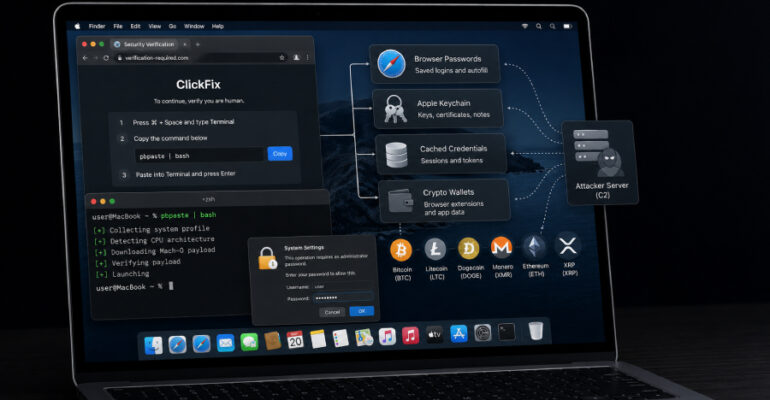
ClickFix Attacks Deliver macOS Stealer That Can Drain Crypto Wallets

ClickFix-style attacks are being used to deliver a Go-based malware capable of stealing cryptocurrency assets, as well as browser-stored passwords, Apple iCloud Keychain data, and cached credentials. The macOS-focused infection chain is designed to deliver a shell script that profiles

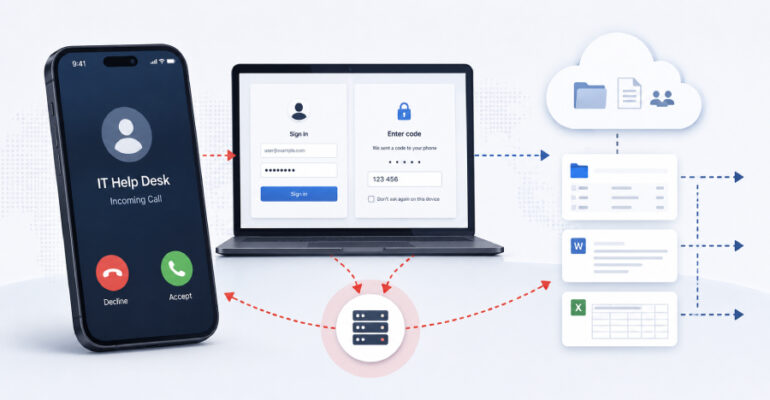
UNC6671 Vishing Attacks Target Personal Phones to Steal SaaS Data

A recent wave of cyber attacks targeting financial services, private equity, and professional services is attributed to a data extortion group known as UNC6671. “UNC6671 continues to rely on voice phishing (vishing) to target enterprise employees, posing as IT help

New WordPress Pre-Auth XSS Could Lead to PHP Code Execution – Patch ASAP

WordPress has fixed a pre-authentication reflected cross-site scripting (XSS) flaw in its login screen that affects every version of the content management system. Under additional conditions, the bug can be chained into PHP code execution on the server. Tracked as CVE-2026-64638 (CVSS

Growing Up The Hard Way

Open Source had a great childhood. For two decades it got to be a kid. It ran around barefoot, gave everything away, trusted strangers, and never once thought about who was watching. It ran the kind of lemonade stand that

18-Year-Old Linux SCTP Flaw Could Let Local Users Gain Root and Escape Containers

A use-after-free bug in Linux’s SCTP networking code can be turned into full root on a host, and Tencent researchers say they used it to escape a container and reach the machine underneath. The flaw has existed since 2008. The

Microsoft 365 AitM Phishing Hijacks Accounts to Collect Payroll and Finance Emails

Cybersecurity researchers have called attention to an active “widespread email-driven phishing campaign” that employs adversary-in-the-middle (AitM) techniques to take control of Microsoft 365 accounts with an aim to identify key personnel involved in financial workflows and gather related email. “The

AI-Assisted HTTP Terminator Finds Novel HTTP Desync Techniques and Apache Zero-Day

PortSwigger says HTTP Terminator, an artificial intelligence (AI)-assisted research system built by James Kettle, generated and proved new HTTP desynchronization techniques after exploring 30,000 candidate attack vectors. PortSwigger said a separate human-guided discovery cascade also exposed a zero-day in Apache

New NatJack Attacks Hijack TCP Sessions and Spoof DNS by Manipulating NAT Tables

Security researcher Malcolm Stagg has disclosed a new attack class called NatJack that manipulates network address translation (NAT) connection state to hijack active TCP sessions, spoof DNS responses, expose mapped ports, and exhaust NAT tables. Presented at Black Hat USA 2026, the

Malware Can Abuse Windows Hello for Business Keys for Persistent Entra ID Access

Security researcher Malcolm Stagg has disclosed a new attack class called NatJack that manipulates network address translation (NAT) connection state to hijack active TCP sessions, spoof DNS responses, disclose victim IP addresses and mapped ports, and exhaust NAT tables. Presented at Black