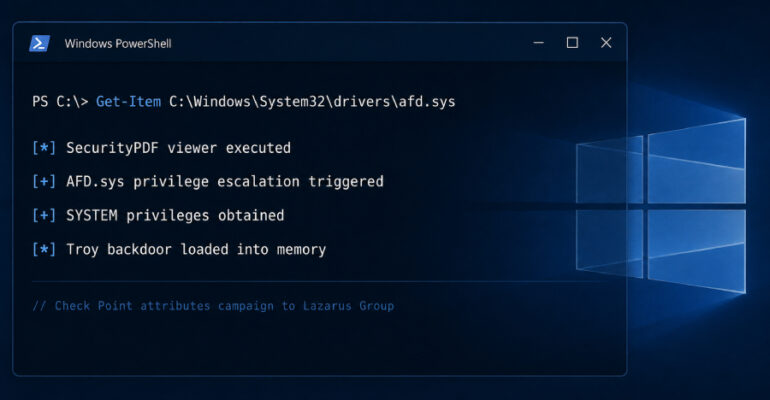
Lazarus Exploits Windows Zero-Day to Gain SYSTEM Access and Deploy Backdoor

The North Korean threat actor known as Lazarus Group has been attributed to the zero-day exploitation of a newly patched security flaw impacting Microsoft Windows to deliver a never-before-seen backdoor targeting defense and aerospace companies across France, Germany, Brazil, and
737 Chrome VPN Extensions Caught Routing Traffic Through Proxies. Check If You Have One

A massive set of 737 free VPN and proxy extensions have been found to mainly target Russian-speaking users seeking access to blocked services with an aim to intercept browser traffic and route them through a proxy infrastructure. The extensions, published

OpenAI, Anthropic, Google API Flaw Let Weaker AI Models Decode Stronger Models’ Reasoning

A newly disclosed flaw in the way OpenAI, Anthropic, and Google carried hidden AI reasoning between API calls let researchers recover internal reasoning and secrets from session logs, including API keys and passwords. The weakness affected encrypted reasoning objects used

Enterprise Defenses Recovered at the Edge and Collapsed Inside

Enterprise defenses are tuned to catch the attacks that make noise. This year’s data shows attackers winning by making none. According to Picus Labs’ new Blue Report 2026, which measured more than 338 million real attack simulations across actual client

Adobe Patches Three CVSS 10.0 ColdFusion and Campaign Classic Flaws

Adobe has shipped updates to address multiple critical security vulnerabilities impacting ColdFusion, Commerce, and Campaign Classic that, if successfully exploited, could result in arbitrary code execution and privilege escalation. The most severe of the flaws are listed below – CVE-2026-48362

Attackers Exploit VMware vCenter Vulnerability to Gain Persistent Remote Access

Threat actors have begun to actively exploit a recently patched critical security flaw in Broadcom VMware vCenter, according to new findings from QUIRSO. The vulnerability in question is CVE-2026-59310 (CVSS score: 9.8), a directory-traversal vulnerability in the VMware vCenter server

Malicious LiteLLM Releases Tied to Trivy Hack May Have Exposed 2,100+ Organizations

Two malicious LiteLLM releases sat on PyPI for about 40 minutes in March carrying credential-stealing code capable of harvesting cloud keys, SSH keys, Kubernetes tokens, database passwords, and other secrets from systems that installed them. Threat intelligence firm CloudSEK now

SAP Commerce Cloud Flaw Could Let Unauthenticated Attackers Execute Arbitrary Code

SAP has released patches to address a maximum-severity security flaw impacting Commerce Cloud (Data Hub Adapter) that could result in arbitrary code execution. The vulnerability, assigned the CVE identifier CVE-2026-58231, is rated 10.0 on the CVSS scoring system. It has

ShieldBreak Zero-Day PoC Claims Microsoft Defender Patch Bypass With SYSTEM Access

The security researcher going by the name Chaotic Eclipse (aka INFINITE NIGHTMARE, MSNightmare, and Nightmare-Eclipse) has released a proof-of-concept (PoC) for a new Microsoft zero-day called ShieldBreak. The vulnerability, rooted in Microsoft Defender for Windows, demonstrates a patch bypass for

Cisco ASA and FTD Flaw Exploited in the Wild Can Trigger Remote DoS

Cisco has warned that a new vulnerability impacting Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software has been exploited in the wild. The high-severity flaw, tracked as CVE-2026-20349 (CVSS score: 8.6), is a case