CDN Tsunami Attack Abuses HTTP/3 Translation for Up to 350x DoS Amplification

Cybersecurity researchers have disclosed two denial-of-service (DoS) attacks that exploit how major content delivery networks (CDNs) convert client-facing HTTP/3 traffic into HTTP/1.1 requests to the websites they front, amplifying a low-bandwidth request stream by up to 350x against the origin
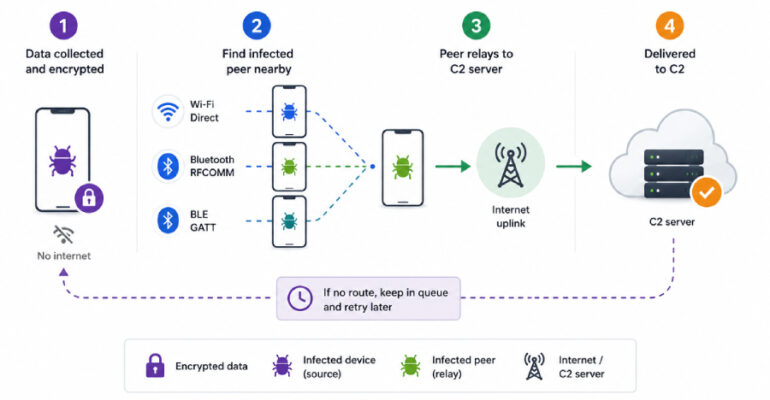
Manic Android Malware Exfiltrates Data From Offline Phones via Nearby Infected Devices

A new Android threat codenamed Manic has been observed actively targeting Ukrainian banks, government and identity services, and messaging applications, as well as Russian and European financial institutions, global fintech and cryptocurrency services, and military-focused communications. “Manic sits at the

NASA AIT-GUI Flaws Could Let Unauthenticated Attackers Issue Spacecraft Commands

Security researchers at Cycode have disclosed a chain of flaws in AIT-GUI, the browser-based operator console for NASA/JPL’s open-source AMMOS Instrument Toolkit, that allow an unauthenticated attacker to issue arbitrary commands to the software’s spacecraft and instrument command bus. The

ToxicPanda 2.0 and GoldDigger Expand Android Banking Attacks with On-Device Fraud

Cybersecurity researchers have shed light on an updated version of ToxicPanda (aka TgToxic) that comes with “significant enhancements,” including a set of 167 remote commands and expands its targeting footprint globally. Zimperium zLabs, in a Wednesday report, said the Android

40 Malicious Firefox Extensions Pose as Web3 Products to Steal Wallet Secrets

A set of 40 Mozilla Firefox extensions has been found to engage in cryptocurrency wallet theft by masquerading as OKX, Rabby Wallet, TronLink, and other Web3 products. According to the Socket Threat Research team, the extensions are part of a

Elementor Pro Flaw Could Let Unauthenticated Attackers Upload PHP and Execute Code

Cybersecurity researchers have disclosed details of a critical flaw in the Elementor Pro WordPress plugin that, if successfully exploited, could lead to remote code execution. The vulnerability, tracked as CVE-2026-32475, carries a CVSS score of 9.0 out of 10.0. It