
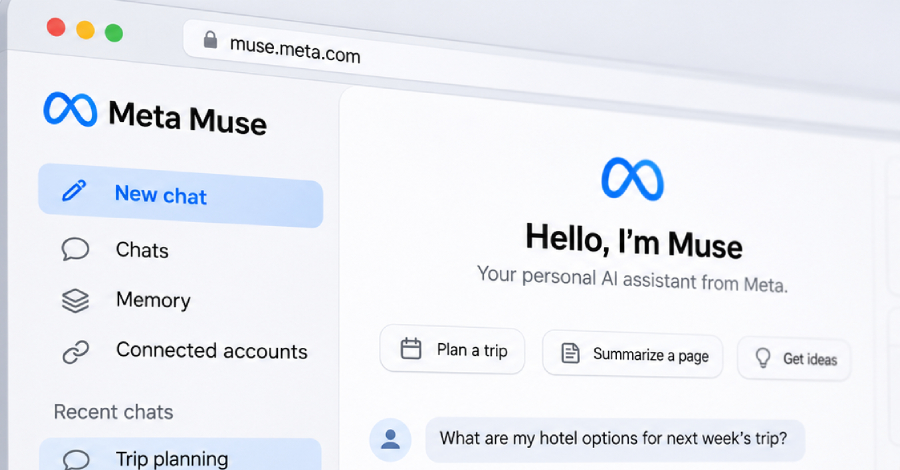
A malicious webpage could extract a Meta Muse user’s private conversations and stored memories from the assistant without triggering any approval prompt, researchers have shown.
The same attack could be extended to reach the credentials Muse stores for the user’s connected accounts.
The work was a laboratory demonstration, not an attack on real users, and it stayed inside the individual user’s…
Read the rest of the story at Read More
Source: The Hacker News


Recent News


Leave a Comment