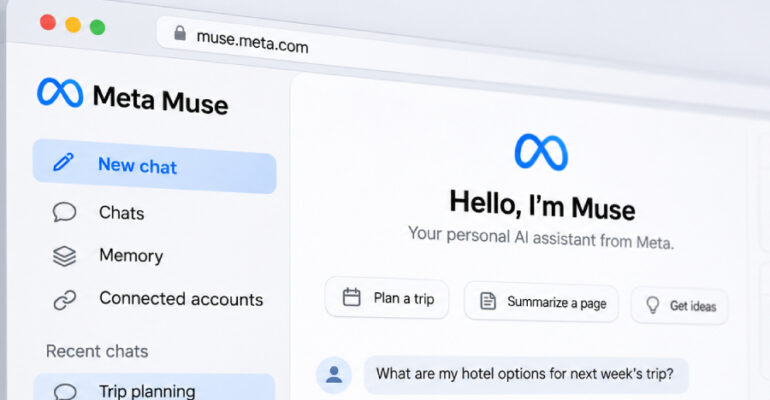
A Single Malicious Webpage Let Researchers Hijack Meta Muse and Access Private Chats

A malicious webpage could extract a Meta Muse user’s private conversations and stored memories from the assistant without triggering any approval prompt, researchers have shown. The same attack could be extended to reach the credentials Muse stores for the user’s
GnuPG Warns Critical GPGME Flaw Could Expose App Data via Malicious OpenPGP Keys

A malicious OpenPGP key with an unusually long user ID can trigger a critical memory bug in GPGME, the standard library that programs use to work with GnuPG. The GnuPG project warned yesterday that the flaw could be used to

Attackers’ AI Agents Found a Zero-Day in Medical-Imaging Software and Gained Root Access

Suspected China-linked hackers used autonomous AI agents to find a previously unknown flaw in MONAI Label, an open-source medical imaging server, and gain root access to a university server, Amazon Threat Intelligence said this week. The flaw allows an attacker

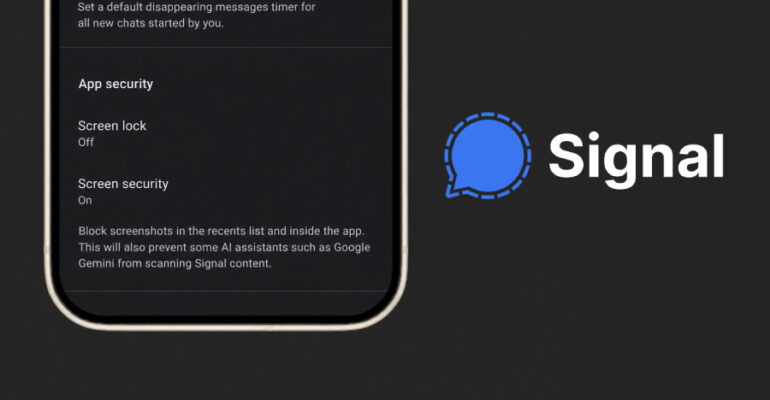
Signal Blocks AI Agents From Reading Private Chats via Screenshots on Android and iOS

Signal has announced that it will restrict screenshots by default to stop artificial intelligence (AI) agents from reading private chats on Android and iOS devices, but conceded that the protection is “incomplete.” The feature applies to agentic systems built into

Hackers Exploit Critical VMware, Cisco, and Apache Flaws as Espionage Attacks Emerge

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added four flaws impacting Apache Roller, Cisco Expressway, SAP NetWeaver, and Broadcom VMware vCenter to its Known Exploited Vulnerabilities (KEV), citing evidence of active exploitation. The vulnerabilities are listed below