Hackers Hijack Five OVHcloud CLI Releases to Distribute Secret-Stealing Malware

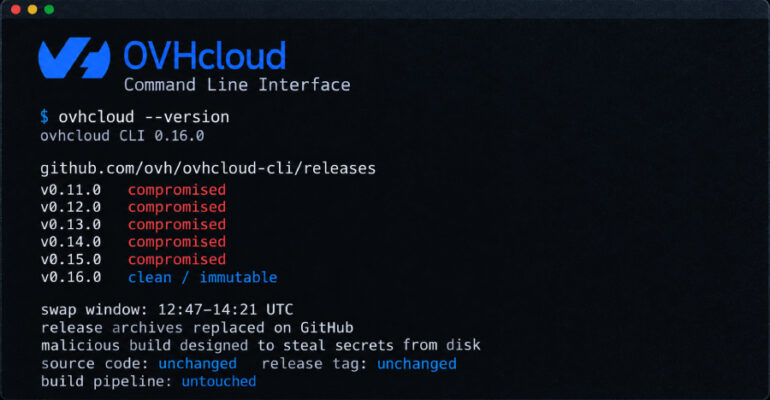
An attacker used a contributor’s GitHub account to replace the download archives on five existing releases of OVHcloud’s command-line tool on Monday, October 19. The account had been hijacked, and the new files were a build designed to steal secrets
ClickFix Attackers Exploit Siemens Software Center Flaw to Deploy Remote Access Trojan

Siemens has addressed a DLL sideloading vulnerability impacting Siemens Software Center that it said has been exploited in ClickFix attacks. The high-severity vulnerability, tracked as CVE-2026-110936 (CVSS v4 score: 8.4), could allow an attacker to place a specially-crafted DLL in

Ex-OpenAI Engineer Detained in Spy Device Case as Saudi Royal Contacts Emerge

A U.S. court on Monday granted the U.S. government’s request to detain a former OpenAI engineer accused of planting a recording device in an executive conference room at the company’s San Francisco office to allegedly steal sensitive secrets. In a

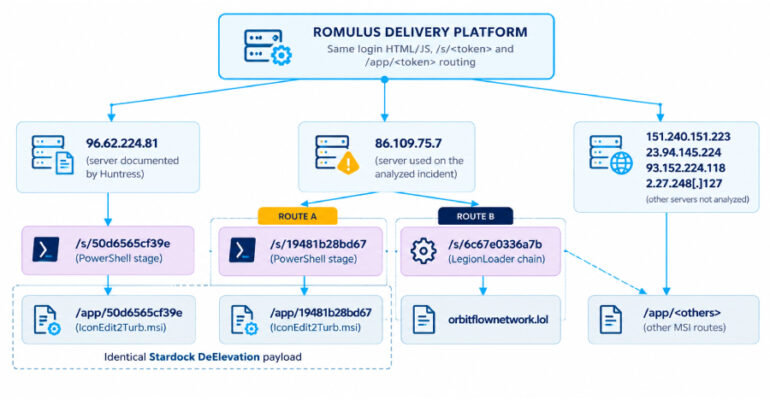
Hackers Use New ROMULUS ClickFix Platform to Deliver LegionLoader and Other Malware

Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that’s being used to distribute malware such as Legion Loader. According to Forescout Research – Vedere Labs, ROMULUS is akin to a malware delivery service that employs ClickFix-style