Google, Anthropic, and OpenAI Unveil Cyber AI Models, Safeguards, and Access Programs

Google on Wednesday announced Gemini 3.8 Flash Cyber, which it described as its most capable cybersecurity model, and has made it available to a set of trusted defenders via a new initiative called the Fairwind Program. “The Fairwind Program gives
Fake Software Installers Disable Windows Update and Weaken Microsoft Defender

An active malware campaign is using bogus software-download websites to impersonate trusted vendors and distribute malicious installers. “The campaign has targeted users looking to download popular software and has resulted in compromises across multiple organizations and industries, primarily affecting China-based

Malicious .git Configs Can Make Claude, Codex, Cursor, and Other AI Agents Run Attacker Code

Manifold Security has disclosed eight security flaws across seven command-line AI coding agents in which a repository’s own Git configuration names a command that the agent runs on the developer’s machine, four of them still unpatched at publication. The command

Malicious Apache Modules Hijack Brazilian Government Site Traffic to Push Betting Pages

A Chinese-speaking cybercrime cluster known as Gambling Goblin has been observed installing malicious Apache modules on compromised web servers run by Brazilian government and educational institutions, and using them to divert visitors to attacker-controlled pages promoting online gambling and sports

BGP Hijack Delivers Malicious Virtualizor Update That Establishes Persistent Root Access

Virtualizor said hackers used a Border Gateway Protocol (BGP) hijack to divert Softaculous traffic. The hackers then used the diverted update traffic to deliver a malicious Virtualizor package to some installations. A hosting-provider account separately said 5 of its 34

Meta Ads Push StreamRat Android Trojan That Can Gain Near-Complete Device Control

Cybersecurity researchers have disclosed details of a new Android banking trojan called StreamRat that was promoted to Spanish-speaking users through a fake television-streaming campaign on Meta and can give operators near-complete control of infected devices. ThreatFabric said the campaign’s advertisement

How to Secure Enterprise AI: From Adoption to Incident Readiness

The debate about whether AI delivers business value is over. The challenge now is implementing it at scale and securely across every function while meeting board-level pressure to move fast. Organizations must focus on adopting AI at business speed without

Attackers Exploit Two SonicWall SMA 1000 Zero-Days That May Form an Attack Chain

SonicWall has released security updates to address two security flaws impacting its Secure Mobile Access (SMA) 1000 series VPN appliances that have been exploited in zero-day attacks. The vulnerabilities, discovered internally by SonicWall’s William Perry and Adam Babis, are listed

GeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends

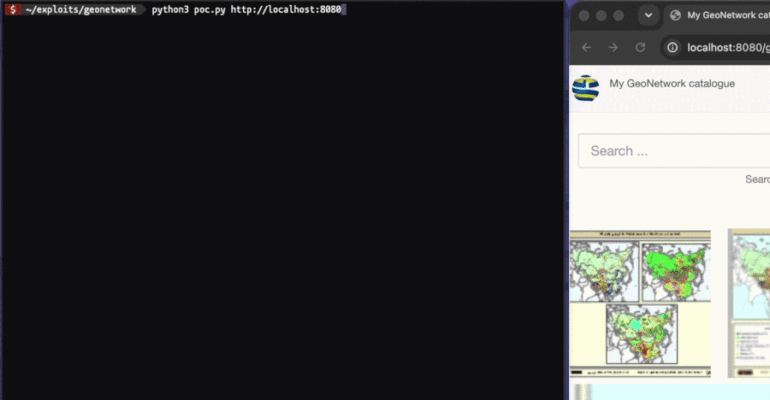
Two vulnerabilities in GeoNetwork can be chained to achieve unauthenticated remote code execution (RCE) on the open-source geospatial metadata catalog, which sits behind many government and agency geoportals. The project shipped fixes in versions 4.4.12 and 4.2.17 on July 8,

Extradited Russian Hacker Faces Charges Over Excel Malware Campaign That Infected Thousands

The U.S. Department of Justice (DoJ) has charged a Russian national, extradited from Cyprus on August 28, with using roughly 255 fake accounts on a freelance platform to send malware-laced Excel attachments to about 80,000 of its users in 2016