Fake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDR

A fake LastPass Authenticator installer offered on GitHub installs a Windows kernel driver that shuts off antivirus and other security software before a password stealer runs if a victim downloads and runs it, researchers at LastPass and Delphos Labs said
Contagious Interview Campaign Compromises 30,000 Devices, Steals $10.71M in Crypto

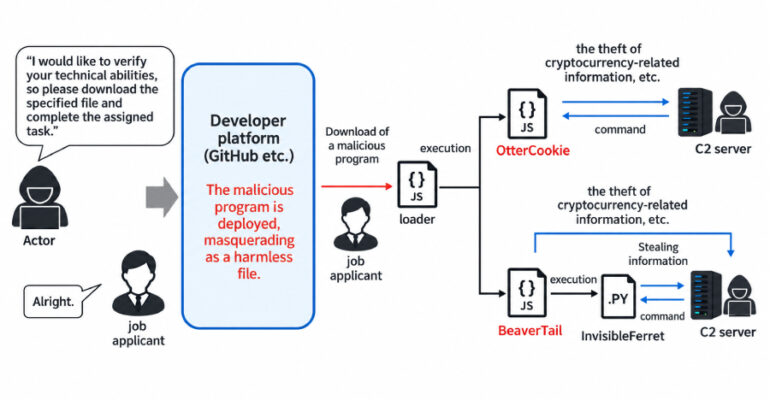
The North Korean threat actors behind the Contagious Interview campaign have compromised at least 30,000 devices located in more than 100 countries and siphoned funds or account credentials from over 7,000 cryptocurrency wallets, according to a new joint cybersecurity advisory.

Google Fined €403 Million Over GDPR Violations Tied to Location Data

Google has been fined €403 million for breaking the EU’s data protection law, the GDPR, in the way three of its features handled people’s location data from May 2018 to February 2020. Ireland’s Data Protection Commission (DPC), Google’s lead regulator in the

⚡ Weekly Recap: Cisco 0-Day, AI Agent RCE, ClickFix Attacks, ClickFix Surge, and Browser Hijacks

A browser. A plugin. A package. A login screen. Normal stuff. That is basically the problem this week. The trouble keeps showing up inside things people already trust: code that takes a bad turn, old payloads coming back, exposed systems,

TASK#STOMP PowerShell Backdoor Steals Documents, Wi-Fi Passwords, and Clipboard Data

Cybersecurity researchers have disclosed details of a new campaign dubbed TASK#STOMP that delivers a PowerShell backdoor designed to harvest sensitive data from compromised hosts. The backdoor “automatically harvests and exfiltrates business documents, watches the filesystem for new files in real

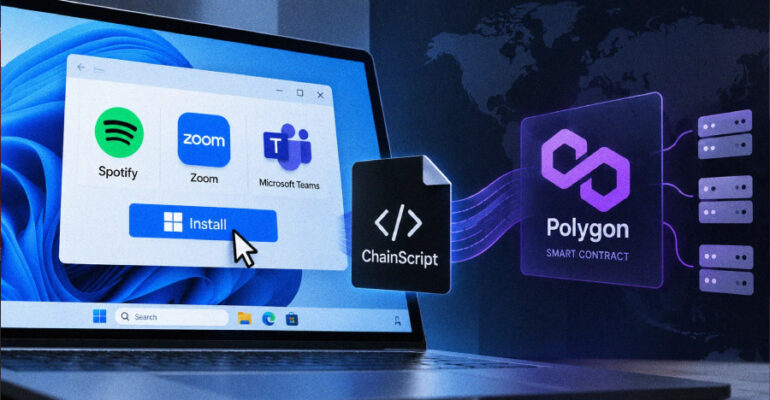
ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure

Threat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript. “ChainScript has appeared under multiple build names, including ComponentTask33, UpdateDigital, HostShared, and OrchidViolet66, while presenting itself as Spotify, Zoom Workplace, and Microsoft Teams

Jade Sleet Linked to Indian IT Provider Breach With FLATROOF and ROOFDECK Backdoors

The North Korean threat actor known as Jade Sleet has been attributed to the compromise of an India-based “much smaller organization” in the information technology (IT) services industry, once again highlighting how the adversary continues to target developers to breach