Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells

Google is warning of renewed mass exploitation of a known security vulnerability in Oracle PeopleSoft as part of a campaign targeting multiple sectors globally. The ShinyHunters-linked activity involves the weaponization of CVE-2026-35273 (CVSS score: 9.8), a critical security flaw that
Zero Trust for AI Agents Starts With Fixing Zero Visibility

The way we talk about AI agents is shifting, and the way we implement them requires an even more fundamental shift. While earlier discourse focused on how quickly organizations could stand up agents and how much productivity they could promise,

Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link

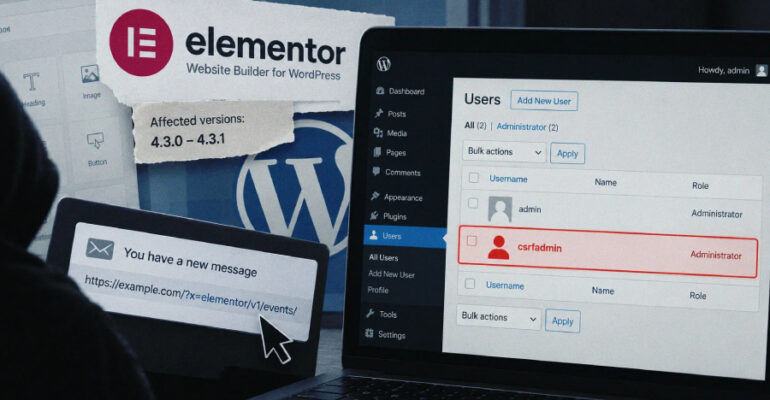
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control of a site. The cross-site request forgery (CSRF) vulnerability,

SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities in question are as follows –

Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack

Kiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat intelligence about an imminent cyber attack. “Kiteworks received credible threat intelligence from federal intelligence authorities