Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks

Apple has released security updates to address a vulnerability in older versions of iOS, iPadOS, and macOS that it said may have been exploited in targeted attacks. The vulnerability, tracked as CVE-2026-86950, refers to an out-of-bounds write impacting the CoreGraphics
Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks

Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis. The malware has been seen in a small number of targeted intrusions at telecommunications organizations, universities, medical

IAM for AI agents: A Practical Enterprise Framework

What is IAM for AI agents? AI agents authenticate, invoke tools, and act across enterprise systems with delegated authority. IAM for AI Agents is the identity-control architecture that governs those actors. This guide covers the limits of conventional provisioning, the

Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M

The attacker who stole about $388 million from the cryptocurrency exchange Bitget gained access through a vulnerability in a third-party security product the exchange used, Bitget said on Monday. The attacker exploited the flaw to obtain high-level internal credentials and

RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims

RatHat’s operators build and publish the Android banking trojan and control infected phones from a web console, according to security company Cleafy. Cleafy has traced nearly 100 deployments of that console since April 2026. It said this fits a malware-as-a-service model, in

⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats

A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into live attack surface. Elsewhere, weak service

Webinar: How to Govern AI Agents, Reduce Excessive Access, and Control Shadow AI

AI agents are moving into production faster than security teams can govern them. They are connecting to apps, handling data, calling APIs, and acting across business systems—often without the same controls applied to human users. According to Okta’s Global CISO

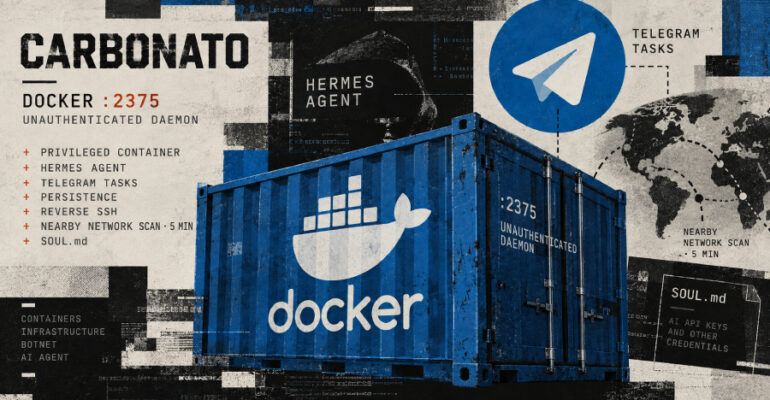
Carbonato Botnet Compromises Docker Hosts to Deploy Telegram-Controlled Hermes AI Agent

Cybersecurity researchers have disclosed details of a new botnet malware called Carbonato that’s targeting exposed Docker daemons to deploy an open-source artificial intelligence (AI) agent framework called Hermes Agent. “The implant installs the framework unchanged, then overwrites its SOUL.md persona

JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources

The threat actor known as JADEPUFFER has been observed orchestrating destructive actions within a Microsoft Azure environment using compromised service principals. Microsoft, which is tracking the activity under the name Storm-3168, has called it an evolution of the threat actor’s

CISA Says Attackers Are Exploiting Two Critical Citrix NetScaler Flaws Globally

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Sunday added two critical Citrix NetScaler ADC and Gateway flaws to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerabilities are listed below – CVE-2026-88771 (CVSS score: