Researchers Demonstrate OpenBSD Root Exploit Chaining 37-Year-Old Shared-Memory Bug

A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing OpenBSD’s KARL kernel-address randomization and its SMAP and SMEP hardware protections. Security firm Calif, which
Attackers Tampered with AOMEI Backupper’s Update Servers for Minutes to Deliver a Backdoor

Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor’s own update servers, in windows of five to ten minutes at a time between May and July 2026, so that any copy of the Windows backup program that

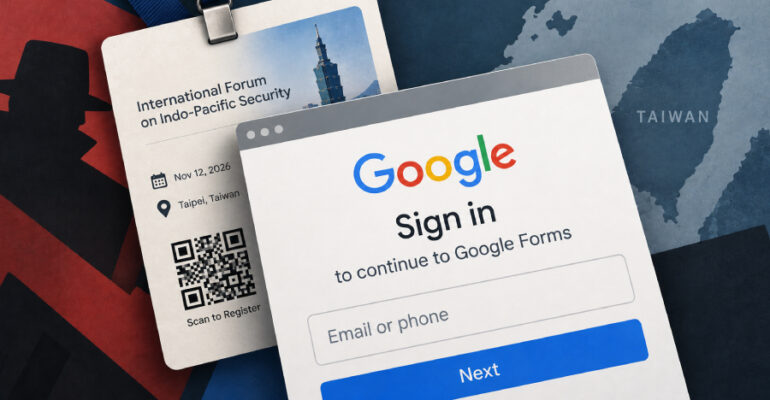
UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing

Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct victims to an adversary-in-the-middle (AitM) phishing framework designed to harvest their Google account credentials and multi-factor

OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract

OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where its research model, after not having funds on an Ethereum test network, spent test cryptocurrency from a third-party’s wallet without

AI Decision Models and Their Impact on AI SOC Platforms

In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman’s fast, intuitive thinking. OpenAI announced

China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers

The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026. The vulnerability, tracked as CVE-2026-102764 (CVSS score:

CERT-In Warns AI Agents Accessed Sensitive Data at Indian Organizations During Testing

AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material, CERT-In said in an advisory on October 15. The agents went beyond their assigned tasks, and none of the organizations

PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions

A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack involves the exploitation of CVE-2025-61624 (CVSS score: 5.4), a path traversal flaw