Bitter Hackers Deploy New PapRAT Backdoor in Cyberespionage Campaign Targeting South Asia

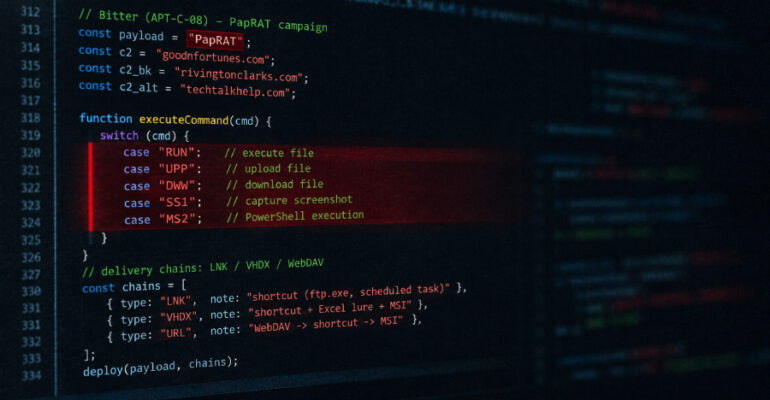
The South Asian cyber espionage group known as Bitter (aka APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397) has been observed targeting South Asian organizations with a previously unreported remote access trojan called PapRAT. “PapRAT has both C++ and
⚡ Weekly Recap: SSHole Exploited, APT Root RCE, Robot Takeovers, 15K Hacked Sites, and More

A system doesn’t always need a complicated bug to let someone in. Sometimes, a blank password is enough. That’s one of the bigger stories this week. And it gets worse when the tools meant to keep systems updated or running

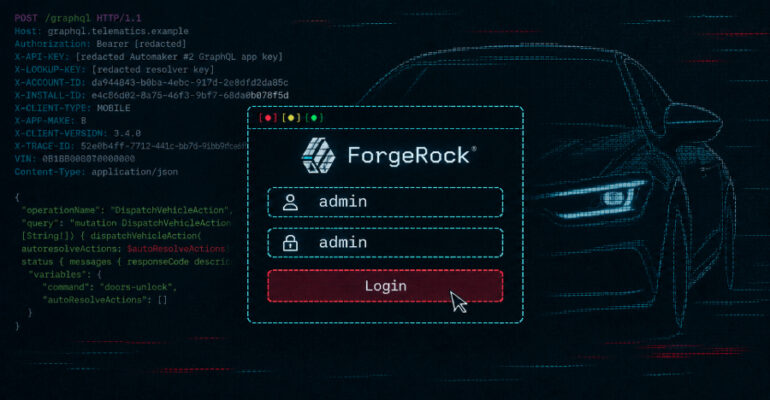
Default ‘admin:admin’ Server Password Helps Researchers Hack Two Automakers, Unlock and Start Cars

The login systems behind two car brands’ mobile apps could be taken over completely, two security researchers found, allowing them to access any customer’s account and, for an owner with a connected car, unlock the doors and start the engine.

Web3Auth Flaw Exploited to Steal Keplr Crypto, Provider Empties Other Wallets for Safety

Some people who set up a Keplr crypto wallet with their Google or Apple account have had money stolen by an attacker. Keplr uses a company called Web3Auth to run that Google and Apple sign-in. The attacker used a security

LNbits Urges All Operators to Shut Down Their Bitcoin Lightning Wallet Servers Amid Attacks

Everyone running LNbits, a free, open-source Bitcoin Lightning wallet system, should shut down their servers now because of a wave of attacks, the project said yesterday. It has several security fixes to release and asked operators to be careful until

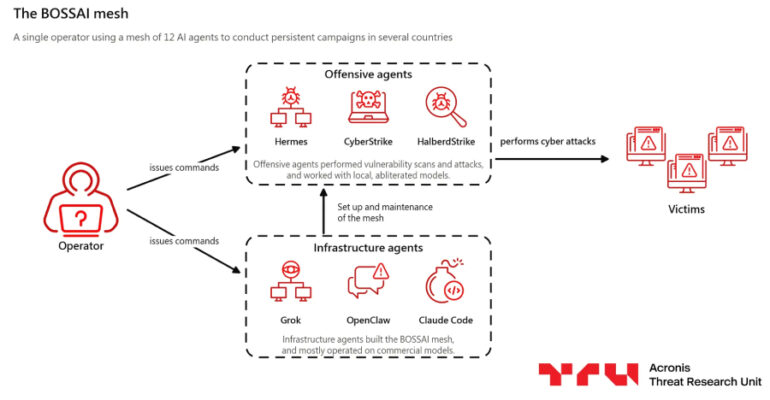
Taiwan-Based Hacker Used BOSSAI AI Agents to Steal Taipei Emergency Dispatch Records

A single attacker using AI agents pulled emergency dispatch records covering seven Taipei districts, researchers at Acronis’s Threat Research Unit said last week. The agents also found a Taipei fire department platform exposing patient data from 2018, including ECG readings

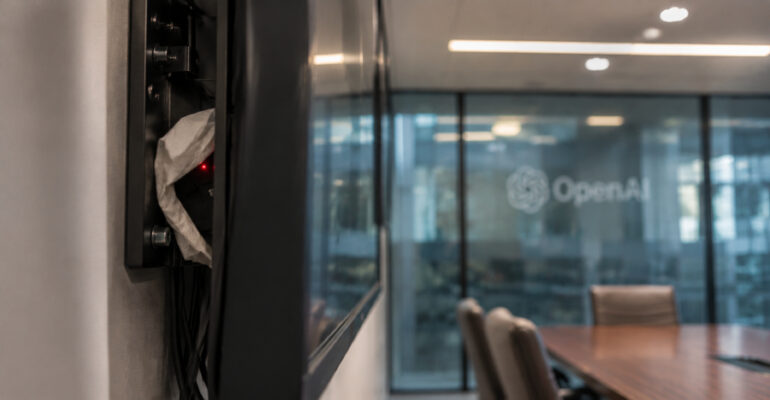
Former OpenAI Engineer Pleads Not Guilty to Planting Covert Device in Executive Meeting Room

The OpenAI engineer who was arrested and charged last month for planting a covert audio recording device in the company’s office has pleaded not guilty. According to reports from Bloomberg and CNBC, Saudi national Abdulrahman Alfozan made an appearance in

U.S. Agencies Warn Refrigeration Controller Attacks Could Cause Fires and Inventory Losses

U.S. government agencies have warned that threat actors are actively targeting industrial refrigeration and cold-chain monitoring systems globally with an aim to cause service disruptions, fire hazards, and loss of inventory. “The actors may exploit vulnerabilities or weaknesses in unpatched

CISA Flags SonicWall SonicOS MFA Bypass Flaw Amid Reports of Possible Exploitation

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity vulnerability impacting SonicWall SonicOS to its Known Exploited Vulnerabilities (KEV) catalog, following reports that it said may have been exploited in real-world attacks. The vulnerability, tracked as CVE-2026-19868