Russian Turla Hackers Use New Cereal Malware to Steal Emails From Government Exchange Servers

The Russia-aligned state-sponsored threat actor known as Turla (aka Snake) is wielding a previously undocumented cyber espionage toolset called Cereal that’s used to break into victims’ Microsoft Exchange servers with an aim to surreptitiously collect emails. According to an ESET
SAP Patches Four CVSS 10.0 Flaws, Including Two Enabling Remote Code Execution

Four flaws that attackers could exploit without logging in were fixed today as part of SAP’s monthly Security Patch Day—the vendor rates all four 10.0, the maximum CVSS score. Three are in the SAP NetWeaver application server, the software SAP

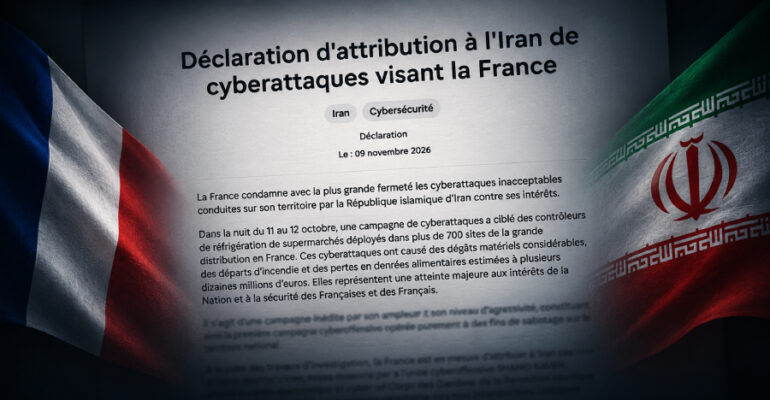
France Blames Iran for Sabotage Attack on Refrigeration Controllers at About 700 Retail Sites

An October cyberattack on refrigeration controllers at about 700 French retail sites was carried out by a cyber unit of Iran’s Islamic Revolutionary Guard Corps (IRGC), the French government said yesterday. The attackers broke into controllers on the night of

Anthropic’s Claude Fable 5.2 Beats GPT-6 Cyber in Multi-Stage Cyberattack Benchmark

Anthropic on Monday released Claude Fable 5.2 and Claude Mythos 5.2 models, which it said exhibit improvements in coding, reasoning, and vision. During pre-release training, the large language models (LLMs) helped its engineers “complete otherwise-infeasible software migrations, designed three working

Google Issues Chrome Security Update for Eighth Actively Exploited Zero-Day of 2026

Google on Monday released updates to patch nine security vulnerabilities, including one that has come under active exploitation in the wild. The high-severity vulnerability, assigned the CVE identifier CVE-2026-125350 (CVSS score: N/A), has been described as a use-after-free bug in

N-able Takes N-central Cloud Offline After Researcher Discloses 33 Zero-Days with PoC Exploits

N-able said it has taken N-central Hosted Environments offline and is urging on-premises customers to shut down their servers until further notice following the public disclosure of over 30 vulnerabilities collectively tracked as Able2Shell. “As a precautionary measure, we are

CISA Warns of Active Exploitation of OpenSSH, GPUStack, FreeSWITCH, and IBM Flaws

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added four security flaws impacting GPUStack, SignalWire FreeSwitch, OpenBSD OpenSSH, and IBM Aspera Faspex to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerabilities are listed