Git Patches Flaw That Lets Malicious Repositories Execute Code During Recursive Clones

A flaw in Git can let a malicious repository run an attacker’s code on a computer that clones it recursively, together with its submodules. The Git project fixed it this week in Git 2.56.1, with matching fixes for the 2.50
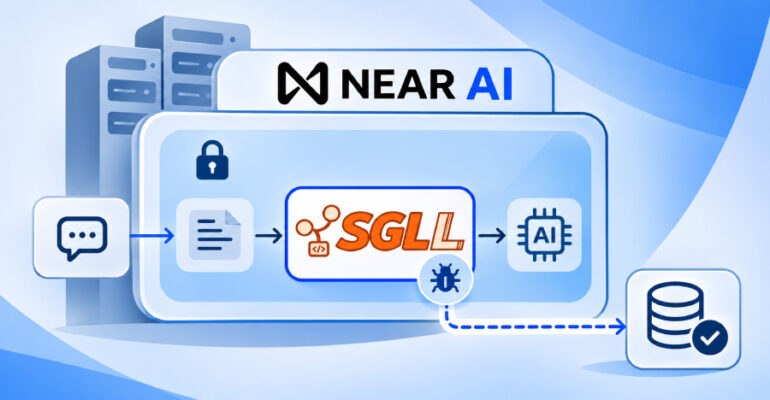
SGLang RCE Exploit Breaches NEAR AI, Steals Data From 18 Agents and About 100 Users

An attacker exploited a remote code execution flaw in SGLang, an open-source inference engine, and ran code on one of NEAR AI’s inference servers last Sunday. The attacker could also have seen requests being processed on that server that day,

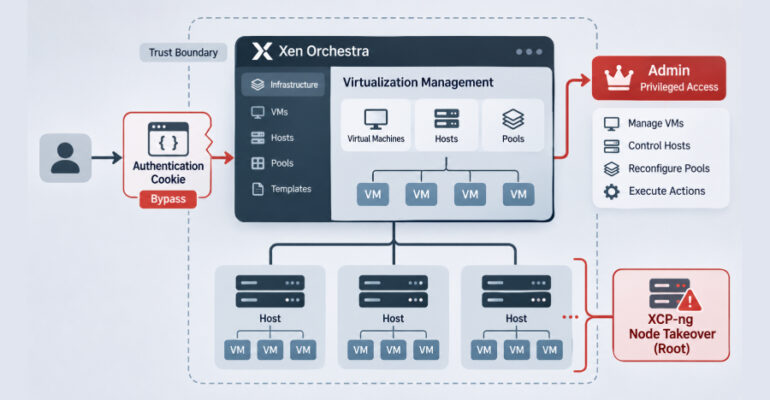
Hackers Exploit Critical Xen Orchestra Auth Bypass Flaw to Gain Admin Access

French software company Vates VMS has warned of a critical security vulnerability in Xen Orchestra that it said is being actively exploited in the wild. The authentication bypass flaw, which does not yet have a CVE identifier, is tracked as

Three China-Nexus Espionage Campaigns Linked Through Sparrow Malware Ecosystem

Three distinct threat activity clusters with shared infrastructure and malware code similarities have been observed targeting telecommunications providers, government organizations, military entities, research institutions, and critical infrastructure across Latin America, Asia, and Europe over the past year. Check Point Research

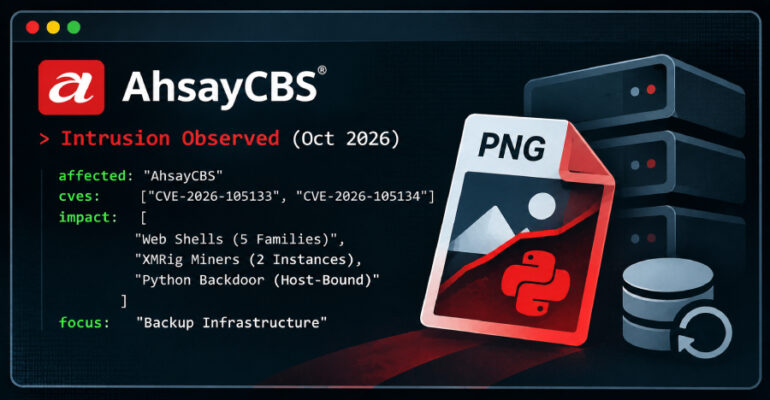
Attackers Exploit AhsayCBS Flaws to Deploy Sandbox-Evading Python Backdoor

Cybersecurity researchers have disclosed details of an attack that exploited two now-patched vulnerabilities in AhsayCBS to deliver a Python-based implant. The activity, observed by Huntress in October 2026, involves the exploitation of a chain comprising CVE-2026-105133 and CVE-2026-105134 to bypass

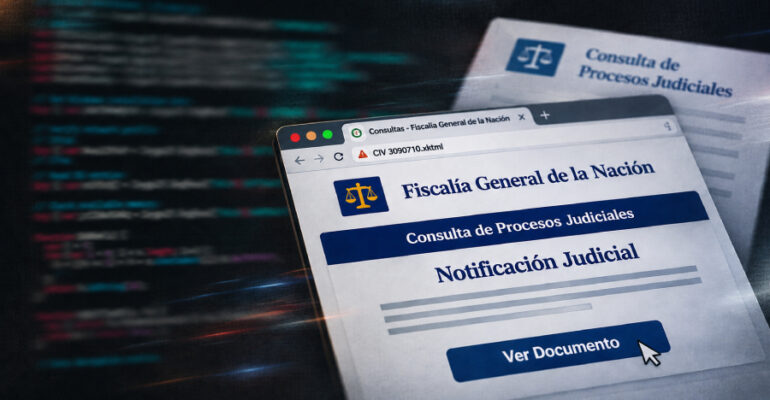
Blind Eagle Uses Fake Court Notices to Deliver Remote Access Trojan Across Latin America

The threat actor known as Blind Eagle has resurfaced with a new campaign targeting organizations in Latin America through judicial and administrative-themed phishing lures to deliver a remote access trojan (RAT) that shares its lineage with AsyncRAT and DCRat. “The

Fireworks AI Breach Widens to Expose Customer Billing Data and Incomplete Model Weights

Fireworks AI disclosed on Monday that its investigation into a security incident first reported early last month  uncovered further malicious activity, affecting account and billing information, alongside secrets, datasets, and incomplete models for a “limited set of accounts.” In a

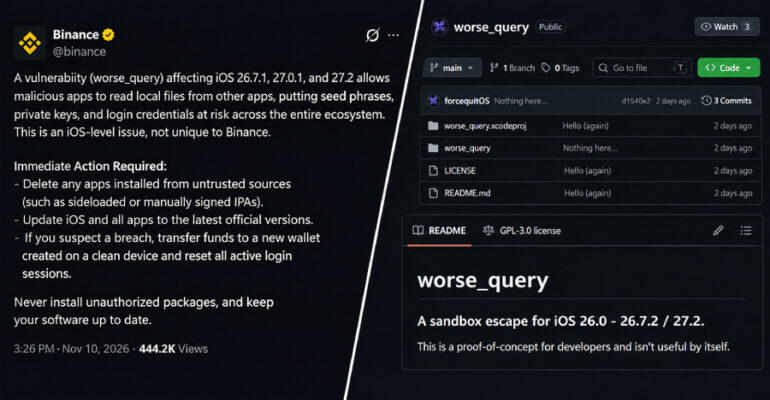
Binance Warns of iOS Sandbox Escape That Could Expose Crypto Wallet Keys, No Fix Confirmed

An iOS sandbox escape published on GitHub lets an app read other apps’ files on iPhones running iOS 26 and 27. That puts seed phrases, private keys, and login credentials at risk of exposure to malicious apps, Binance warned today.

Beyond the Alert: The Case for Rich Network Data

At some point your security will fail. This isn’t pessimism. It’s not because your team and tools aren’t sophisticated enough. It’s the reason we have detections in the first place. And, it’s why once we accept that prevention has its

Apple Patches iMessage Group Chat Privacy Flaws and Bluetooth Pairing Vulnerabilities

An iMessage flaw could let a remote attacker join a group chat and receive its messages, Apple said yesterday, and it released updates to fix it. The updates also fix a separate iMessage flaw that could let someone added to