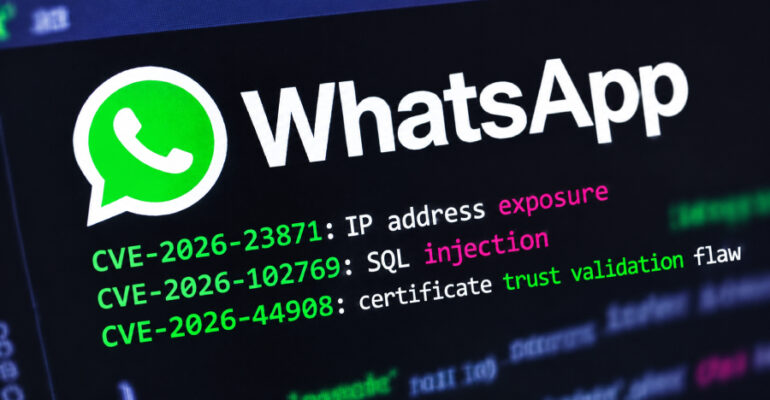
WhatsApp Patches 3 Security Flaws, Including Android Bug Suspected of Use in Scams

Meta-owned WhatsApp has addressed security vulnerabilities, including one impacting its Android app that it suspects may have been exploited in connection with scam messages. The vulnerability, tracked as CVE-2026-23871, has been described as a case of incomplete validation of external
Bazuka Android Malware Uses Fake Screen Overlays to Hide Credential Theft and Device Control

Cybersecurity researchers have disclosed details of a previously unknown Android malware framework called Bazuka that offers large language model (LLM) integration for victim management and control at scale. Dutch mobile security company ThreatFabric said it discovered the threat in late

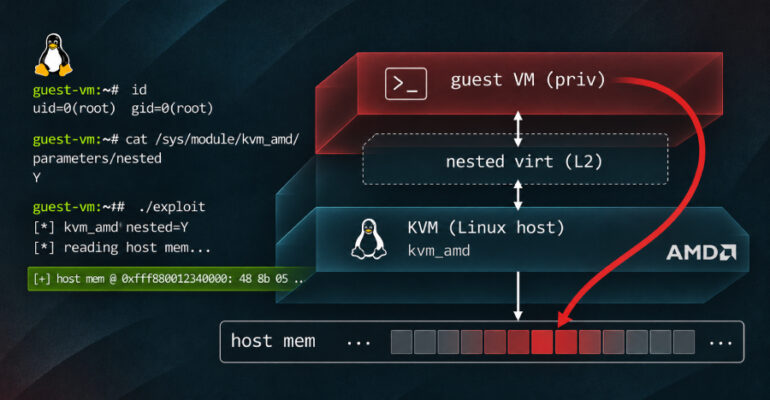
Linux KVM Flaw CVE-2026-99312 Lets Guest VMs Access Host Memory on AMD Hosts

A flaw in KVM, the hypervisor built into the Linux kernel, let researchers read about 127 GB of a cloud server’s memory from inside a virtual machine of their own on DigitalOcean. On a shared server, that memory can include

The Path to AI Autonomy in the SOC

Security leaders are about to hand AI agents a lot more authority. In a recent a16z survey of CISOs at organizations with more than 1,000 employees, 36% said they are comfortable today letting AI agents act autonomously on low-risk security

SonicWall Warns Gen 6 Firewalls Won’t Get Security Patches, Even for Critical Flaws

SonicWall has urged all customers still running Generation 6 firewalls to retire and replace them immediately and stop exposing the devices on the internet edge, citing security risks fueled by AI-assisted attacks. “Attackers now use automation and AI to find

Hackers Exploit Critical Cisco Expressway Flaw, Breach Four Devices and Reach Internal Network

Threat actors have been observed exploiting a recently disclosed critical security flaw in Cisco Expressway to breach a Russian organization shortly after the public release of a proof-of-concept (PoC) exploit. The activity involves the exploitation of CVE-2026-76466 (CVSS score: 9.8),

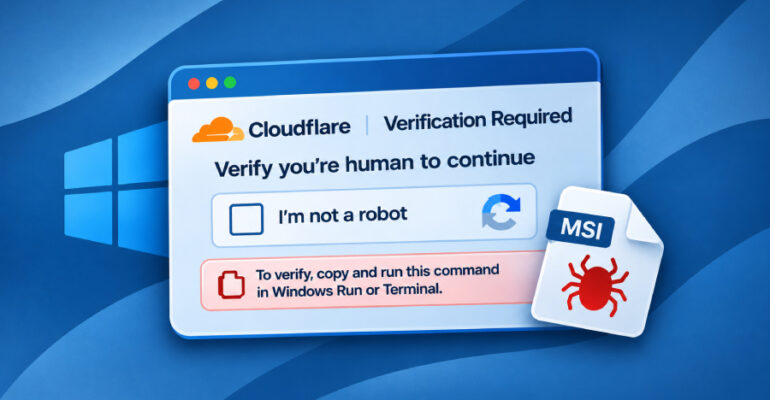
ROMULUS ClickFix Attacks Deliver RAT That Can Spy on Users and Control PCs

Threat actors have been observed using the ROMULUS ClickFix malware delivery platform to deliver a previously undocumented remote access trojan (RAT) that shares similarities with CNCMachineRMS. “ROMULUS likely operates as a delivery service, distributing CNCMachineRMS and Legion Loader through separate

China-Linked Hackers Exploit Critical VMware vCenter Zero-Day to Gain Admin Access and Steal Data

The suspected China-nexus cyber espionage group known as Armory Castle (formerly UNC5221) has been attributed to the zero-day exploitation of a critical security flaw in VMware vCenter Server in early September 2026. The vulnerability, tracked as CVE-2026-123890 (CVSS score: 9.8),

New Unpatched Windows 0-Day FastUnlock Lets Someone Holding a Locked PC Run Programs on It

A newly disclosed unpatched zero-day technique called FastUnlock lets someone with physical access to a locked Windows computer start programs without signing in. Whoever uses it gets only a limited account, not administrator control of the machine. The method was