





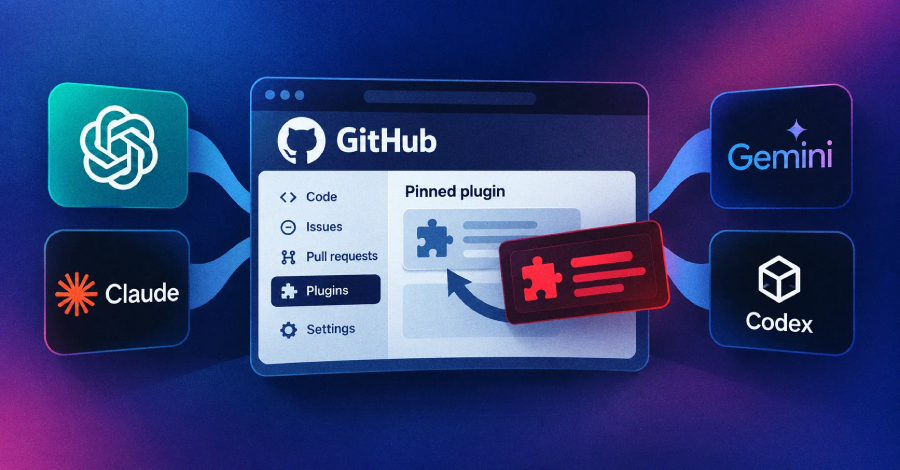
A flaw in four widely used AI coding agents lets someone who controls a plugin’s code repository swap the plugin an agent installs for a malicious one, even when the agent locked that plugin to a specific reviewed version, security firm Air Security said on Thursday.
The firm said Anthropic has patched the flaw in Claude Code 2.1.179 and OpenAI in Codex 0.146.0, that GitHub Copilot has no…
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment