





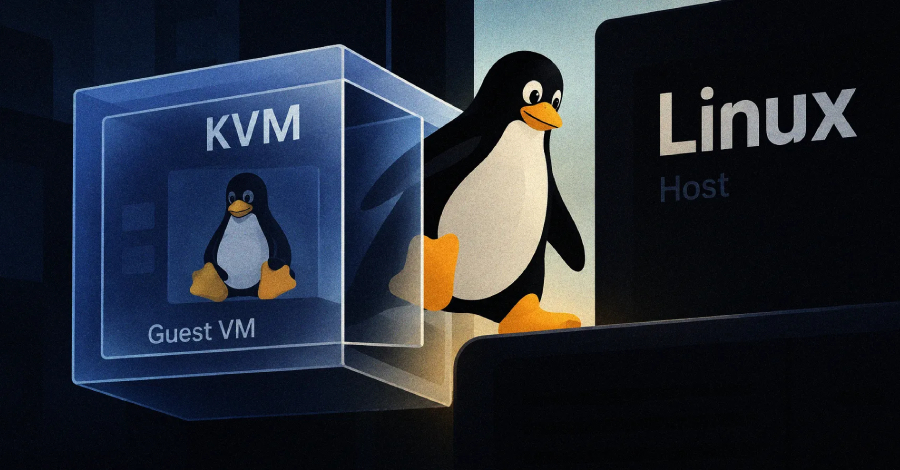
A new flaw in the Linux kernel’s KVM virtualization code for ARM64 processors can leave a freed piece of host memory exposed to a guest virtual machine on hosts with nested virtualization enabled.
The bug, tracked as CVE-2026-89775, allows a guest to read and write host kernel memory, and the researcher who found it says it can be used to escape the guest and run code on the host machine….
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment