
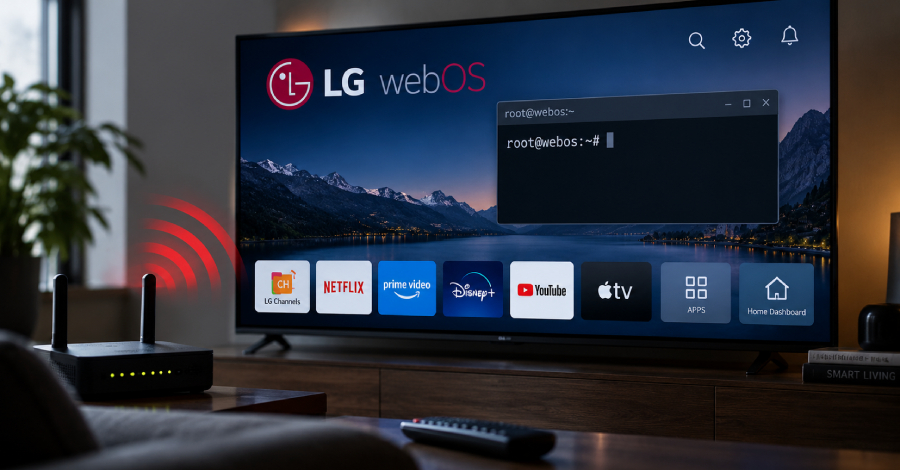
Three vulnerabilities in LG’s webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a PIN or any interaction from the owner.
LG has issued a fix, according to an advisory published by SSD Secure Disclosure on October 12.
The chain was tested on two TV models, the 32LQ636BPSA and the 27TQ600SW, running webOS 7.5.7-25 on firmware…
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment