
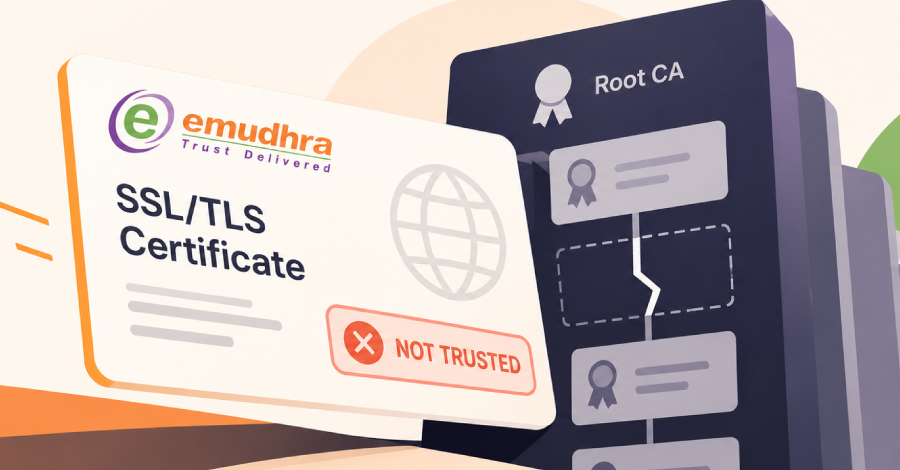
eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days after a researcher reported recovering the private keys of eight of its intermediate CA certificates.
eMudhra said it will replace affected customers’ certificates with free ones from partners, though its…
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment