How to Stop AI Data Leaks: A Webinar Guide to Auditing Modern Agentic Workflows

Artificial Intelligence (AI) is no longer just a tool we talk to; it is a tool that does things for us. These are called AI Agents. They can send emails, move data, and even manage software on their own. But
The Zero-Day Scramble is Avoidable: A Guide to Attack Surface Reduction

You can’t control when the next critical vulnerability drops. You can control how much of your environment is exposed when it does. The problem is that most teams have more internet-facing exposure than they realise. Intruder’s Head of Security digs

APT28 Uses BEARDSHELL and COVENANT Malware to Spy on Ukrainian Military

The Russian state-sponsored hacking group tracked as APT28 has been observed using a pair of implants dubbed BEARDSHELL and COVENANT to facilitate long‑term surveillance of Ukrainian military personnel. The two malware families have been put to use since April 2024,

Threat Actors Mass-Scan Salesforce Experience Cloud via Modified AuraInspector Tool

Salesforce has warned of an increase in threat actor activity that’s aimed at exploiting misconfigurations in publicly accessible Experience Cloud sites by making use of a customized version of an open-source tool called AuraInspector. The activity, per the company, involves

CISA Flags SolarWinds, Ivanti, and Workspace One Vulnerabilities as Actively Exploited

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added three security flaws to its Known Exploited Vulnerabilities (KEV) catalog, based on evidence of active exploitation. The vulnerability list is as follows – CVE-2021-22054 (CVSS score: 7.5) – A

Malicious npm Package Posing as OpenClaw Installer Deploys RAT, Steals macOS Credentials

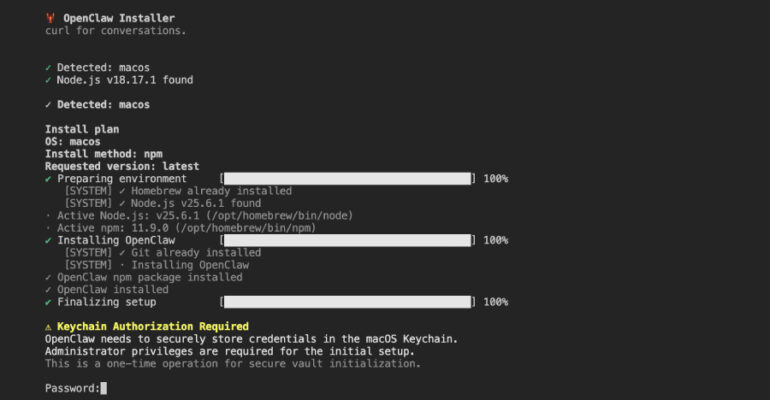
Cybersecurity researchers have discovered a malicious npm package that masquerades as an OpenClaw installer to deploy a remote access trojan (RAT) and steal sensitive data from compromised hosts. The package, named “@openclaw-ai/openclawai,” was uploaded to the registry by a user

UNC4899 Breached Crypto Firm After Developer AirDropped Trojanized File to Work Device

The North Korean threat actor known as UNC4899 is suspected to be behind a sophisticated cloud compromise campaign targeting a cryptocurrency organization in 2025 to steal millions of dollars in cryptocurrency. The activity has been attributed with moderate confidence to

⚡ Weekly Recap: Qualcomm 0-Day, iOS Exploit Chains, AirSnitch Attack & Vibe-Coded Malware

Another week in cybersecurity. Another week of “you’ve got to be kidding me.” Attackers were busy. Defenders were busy. And somewhere in the middle, a whole lot of people had a very bad Monday morning. That’s kind of just how

Can the Security Platform Finally Deliver for the Mid-Market?

Mid-market organizations are constantly striving to achieve security levels on a par with their enterprise peers. With heightened awareness of supply chain attacks, your customers and business partners are defining the security level you must meet. What if you could

Chrome Extension Turns Malicious After Ownership Transfer, Enabling Code Injection and Data Theft

Two Google Chrome extensions have turned malicious after what appears to be a case of ownership transfer, offering attackers a way to push malware to downstream customers, inject arbitrary code, and harvest sensitive data. The extensions in question, both originally