Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks

Threat actors are leveraging the trusted Node.js JavaScript runtime in multiple cyber attacks as a way to deploy malicious payloads. According to a new report published by the Symantec Threat Hunter Team today, the attack method has been put to
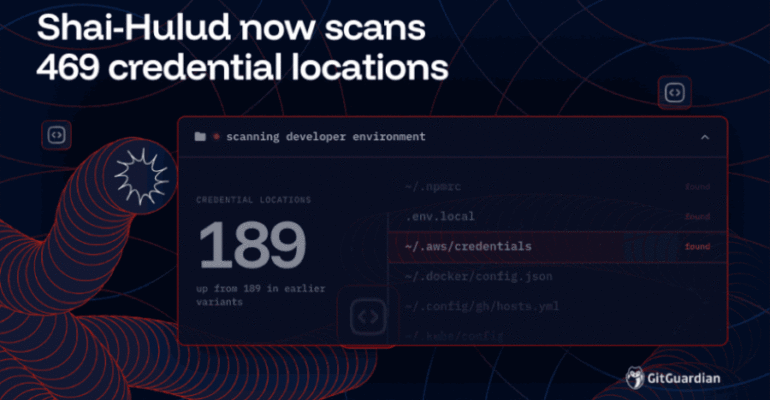
Shai-Hulud’s Reach Just Grew to 469 Credential Locations. Here’s What That Means

In early August, GitGuardian researchers found that a recent Shai-Hulud infostealer worm variant had evolved to scan for credentials across 469 locations across developer environments, Continuous Integration/Continuous Deployment (CI/CD) tooling, cloud configurations, and even AI tool configs. Earlier variants of

Pegasus Zero-Click Spyware Exploit Infects Serbian Student Movement Member’s iPhone

The iPhone belonging to a member of Serbia’s student protest movement was infected with NSO Group’s Pegasus spyware, according to new findings from the Citizen Lab in collaboration with the SHARE Foundation. “Our analysis confirmed that an iMessage zero-click exploit

Researcher Releases FalconFlank PoC Showing Privilege Escalation in CrowdStrike Falcon

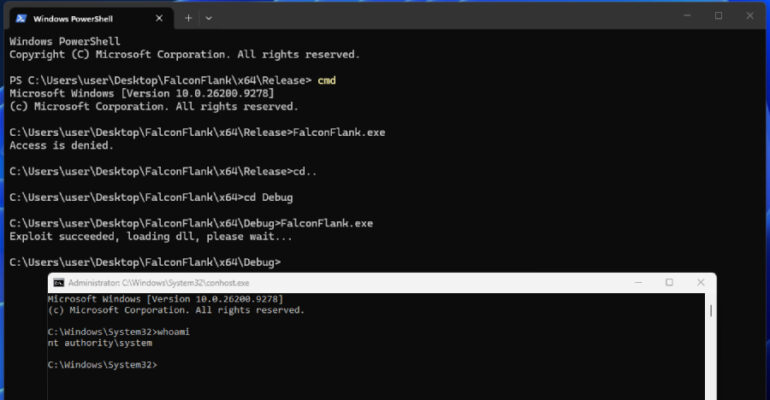
The security researcher known as Chaotic Eclipse (aka INFINITE NIGHTMARE, MSNightmare, and Nightmare-Eclipse) has dropped a new zero-day dubbed FalconFlank, a privilege escalation flaw impacting Crowdstrike Falcon. “FalconFlank is a 0day privilege escalation that abuses the office malicious macros remediation

CISA Adds Seven Exploited Flaws as Attackers Deploy Reverse Shells and Crypto Miners

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added seven security flaws to its Known Exploited Vulnerabilities (KEV) catalog after they landed in attackers’ crosshairs. The vulnerabilities are as follows – CVE-2026-83548 (CVSS score: 10.0) – A server-side

Google, Anthropic, and OpenAI Unveil Cyber AI Models, Safeguards, and Access Programs

Google on Wednesday announced Gemini 3.8 Flash Cyber, which it described as its most capable cybersecurity model, and has made it available to a set of trusted defenders via a new initiative called the Fairwind Program. “The Fairwind Program gives

Fake Software Installers Disable Windows Update and Weaken Microsoft Defender

An active malware campaign is using bogus software-download websites to impersonate trusted vendors and distribute malicious installers. “The campaign has targeted users looking to download popular software and has resulted in compromises across multiple organizations and industries, primarily affecting China-based

Malicious .git Configs Can Make Claude, Codex, Cursor, and Other AI Agents Run Attacker Code

Manifold Security has disclosed eight security flaws across seven command-line AI coding agents in which a repository’s own Git configuration names a command that the agent runs on the developer’s machine, four of them still unpatched at publication. The command

Malicious Apache Modules Hijack Brazilian Government Site Traffic to Push Betting Pages

A Chinese-speaking cybercrime cluster known as Gambling Goblin has been observed installing malicious Apache modules on compromised web servers run by Brazilian government and educational institutions, and using them to divert visitors to attacker-controlled pages promoting online gambling and sports

BGP Hijack Delivers Malicious Virtualizor Update That Establishes Persistent Root Access

Virtualizor said hackers used a Border Gateway Protocol (BGP) hijack to divert Softaculous traffic. The hackers then used the diverted update traffic to deliver a malicious Virtualizor package to some installations. A hosting-provider account separately said 5 of its 34