New RFP Template for AI Usage Control and AI Governance 

As AI becomes the central engine for enterprise productivity, security leaders are finally getting the green light — and the budget — to secure it. But there’s a quiet crisis unfolding in the boardroom: many organizations know they need “AI
Fake Laravel Packages on Packagist Deploy RAT on Windows, macOS, and Linux

Cybersecurity researchers have flagged malicious Packagist PHP packages masquerading as Laravel utilities that act as a conduit for a cross-platform remote access trojan (RAT) that’s functional on Windows, macOS, and Linux systems. The names of the packages are listed below

APT41-Linked Silver Dragon Targets Governments Using Cobalt Strike and Google Drive C2

Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) group dubbed Silver Dragon that has been linked to cyber attacks targeting entities in Europe and Southeast Asia since at least mid-2024. “Silver Dragon gains its initial access by

CISA Adds Actively Exploited VMware Aria Operations Flaw CVE-2026-22719 to KEV Catalog

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a recently disclosed security flaw impacting Broadcom VMware Aria Operations to its Known Exploited Vulnerabilities (KEV) catalog, citing active exploitation in the wild. The high-severity vulnerability, CVE-2026-22719 (CVSS score:

Fake Tech Support Spam Deploys Customized Havoc C2 Across Organizations

Threat hunters have called attention to a new campaign as part of which bad actors masqueraded as fake IT support to deliver the Havoc command-and-control (C2) framework as a precursor to data exfiltration or ransomware attack. The intrusions, identified by

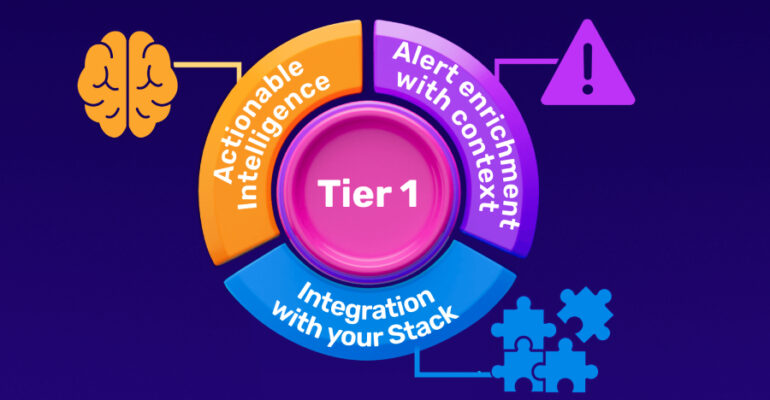
Building a High-Impact Tier 1: The 3 Steps CISOs Must Follow

Every CISO knows the uncomfortable truth about their Security Operations Center: the people most responsible for catching threats in real time are the people with the least experience. Tier 1 analysts sit at the front line of detection, and yet

Open-Source CyberStrikeAI Deployed in AI-Driven FortiGate Attacks Across 55 Countries

The threat actor behind the recently disclosed artificial intelligence (AI)-assisted campaign targeting Fortinet FortiGate appliances leveraged an open-source, AI-native security testing platform called CyberStrikeAI to execute the attacks. The new findings come from Team Cymru, which detected its use following

AI Agents: The Next Wave Identity Dark Matter – Powerful, Invisible, and Unmanaged

The Rise of MCPs in the Enterprise The Model Context Protocol (MCP) is quickly becoming a practical way to push LLMs from “chat” into real work. By providing structured access to applications, APIs, and data, MCP enables prompt-driven AI agents

Starkiller Phishing Suite Uses AitM Reverse Proxy to Bypass Multi-Factor Authentication

Cybersecurity researchers have disclosed details of a new phishing suite called Starkiller that proxies legitimate login pages to bypass multi-factor authentication (MFA) protections. It’s advertised as a cybercrime platform by a threat group calling itself Jinkusu, granting customers access to

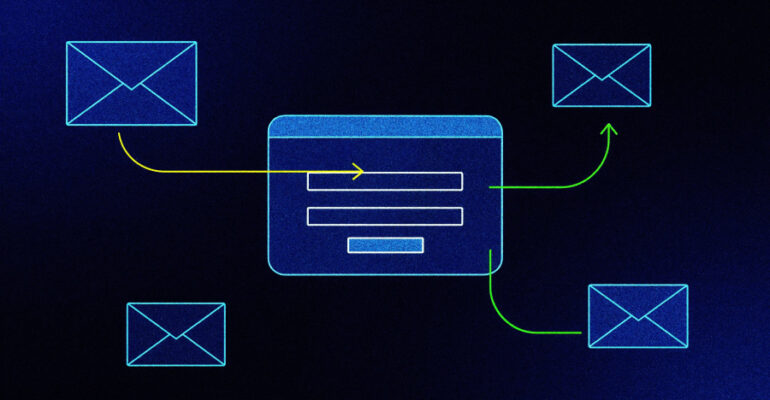
Microsoft Warns OAuth Redirect Abuse Delivers Malware to Government Targets

Microsoft on Monday warned of phishing campaigns that employ phishing emails and OAuth URL redirection mechanisms to bypass conventional phishing defenses implemented in email and browsers. The activity, the company said, targets government and public-sector organizations with the end goal