Safe and Inclusive E‑Society: How Lithuania Is Bracing for AI‑Driven Cyber Fraud

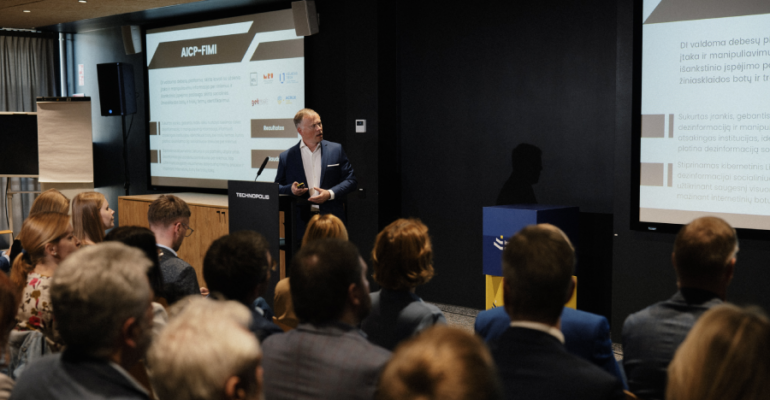
Presentation of the KTU Consortium Mission ‘A Safe and Inclusive Digital Society’ at the Innovation Agency event ‘Innovation Breakfast: How Mission-Oriented Science and Innovation Programmes Will Address Societal Challenges’. Technologies are evolving fast, reshaping economies, governance, and daily life. Yet,
New ZeroDayRAT Mobile Spyware Enables Real-Time Surveillance and Data Theft

Cybersecurity researchers have disclosed details of a new mobile spyware platform dubbed ZeroDayRAT that’s being advertised on Telegram as a way to grab sensitive data and facilitate real-time surveillance on Android and iOS devices. “The developer runs dedicated channels for

New Chrome Zero-Day (CVE-2026-2441) Under Active Attack — Patch Released

Google on Friday released security updates for its Chrome browser to address a security flaw that it said has been exploited in the wild. The high-severity vulnerability, tracked as CVE-2026-2441 (CVSS score: 8.8), has been described as a use-after-free bug

Microsoft Discloses DNS-Based ClickFix Attack Using Nslookup for Malware Staging

Microsoft has disclosed details of a new version of the ClickFix social engineering tactic in which the attackers trick unsuspecting users into running commands that carry out a Domain Name System (DNS) lookup to retrieve the next-stage payload. Specifically, the

Google Ties Suspected Russian Actor to CANFAIL Malware Attacks on Ukrainian Orgs

A previously undocumented threat actor has been attributed to attacks targeting Ukrainian organizations with malware known as CANFAIL. Google Threat Intelligence Group (GTIG) described the hack group as possibly affiliated with Russian intelligence services. The threat actor is assessed to

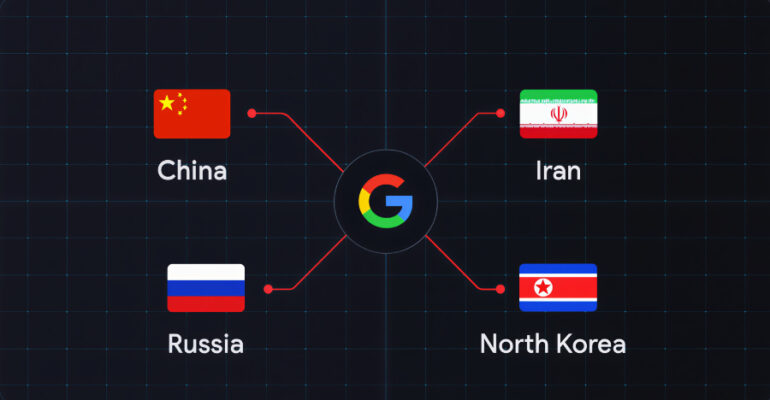
Google Links China, Iran, Russia, North Korea to Coordinated Defense Sector Cyber Operations

Several state-sponsored actors, hacktivist entities, and criminal groups from China, Iran, North Korea, and Russia have trained their sights on the defense industrial base (DIB) sector, according to findings from Google Threat Intelligence Group (GTIG). The tech giant’s threat intelligence

UAT-9921 Deploys VoidLink Malware to Target Technology and Financial Sectors

A previously unknown threat actor tracked as UAT-9921 has been observed leveraging a new modular framework called VoidLink in its campaigns targeting the technology and financial services sectors, according to findings from Cisco Talos. “This threat actor seems to have

Malicious Chrome Extensions Caught Stealing Business Data, Emails, and Browsing History

Cybersecurity researchers have discovered a malicious Google Chrome extension that’s designed to steal data associated with Meta Business Suite and Facebook Business Manager. The extension, named CL Suite by @CLMasters (ID: jkphinfhmfkckkcnifhjiplhfoiefffl), is marketed as a way to scrape Meta

npm’s Update to Harden Their Supply Chain, and Points to Consider

In December 2025, in response to the Sha1-Hulud incident, npm completed a major authentication overhaul intended to reduce supply-chain attacks. While the overhaul is a solid step forward, the changes don’t make npm projects immune from supply-chain attacks. npm is

Researchers Observe In-the-Wild Exploitation of BeyondTrust CVSS 9.9 Vulnerability

Threat actors have started to exploit a recently disclosed critical security flaw impacting BeyondTrust Remote Support (RS) and Privileged Remote Access (PRA) products, according to watchTowr. “Overnight we observed first in-the-wild exploitation of BeyondTrust across our global sensors,” Ryan Dewhurst,