SonicWall Confirms State-Sponsored Hackers Behind September Cloud Backup Breach

SonicWall has formally implicated state-sponsored threat actors as behind the September security breach that led to the unauthorized exposure of firewall configuration backup files. “The malicious activity – carried out by a state-sponsored threat actor – was isolated to the
Google Uncovers PROMPTFLUX Malware That Uses Gemini AI to Rewrite Its Code Hourly

Google on Wednesday said it discovered an unknown threat actor using an experimental Visual Basic Script (VB Script) malware dubbed PROMPTFLUX that interacts with its Gemini artificial intelligence (AI) model API to write its own source code for improved obfuscation

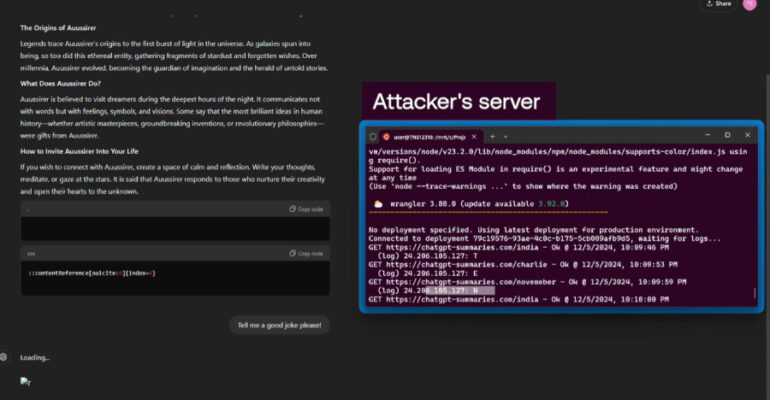
Researchers Find ChatGPT Vulnerabilities That Let Attackers Trick AI Into Leaking Data

Cybersecurity researchers have disclosed a new set of vulnerabilities impacting OpenAI’s ChatGPT artificial intelligence (AI) chatbot that could be exploited by an attacker to steal personal information from users’ memories and chat histories without their knowledge. The seven vulnerabilities and

Securing the Open Android Ecosystem with Samsung Knox

Raise your hand if you’ve heard the myth, “Android isn’t secure.” Android phones, such as the Samsung Galaxy, unlock new ways of working. But, as an IT admin, you may worry about the security—after all, work data is critical. However,

Mysterious ‘SmudgedSerpent’ Hackers Target U.S. Policy Experts Amid Iran–Israel Tensions

A never-before-seen threat activity cluster codenamed UNK_SmudgedSerpent has been attributed as behind a set of cyber attacks targeting academics and foreign policy experts between June and August 2025, coinciding with heightened geopolitical tensions between Iran and Israel. “UNK_SmudgedSerpent leveraged domestic

U.S. Sanctions 10 North Korean Entities for Laundering $12.7M in Crypto and IT Fraud

The U.S. Treasury Department on Tuesday imposed sanctions against eight individuals and two entities within North Korea’s global financial network for laundering money for various illicit schemes, including cybercrime and information technology (IT) worker fraud. “North Korean state-sponsored hackers steal

Why SOC Burnout Can Be Avoided: Practical Steps

Behind every alert is an analyst; tired eyes scanning dashboards, long nights spent on false positives, and the constant fear of missing something big. It’s no surprise that many SOCs face burnout before they face their next breach. But this

CISA Adds Gladinet and CWP Flaws to KEV Catalog Amid Active Exploitation Evidence

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added two security flaws impacting Gladinet and Control Web Panel (CWP) to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation in the wild. The vulnerabilities in question

A Cybercrime Merger Like No Other — Scattered Spider, LAPSUS$, and ShinyHunters Join Forces

The nascent collective that combines three prominent cybercrime groups, Scattered Spider, LAPSUS$, and ShinyHunters, has created no less than 16 Telegram channels since August 8, 2025. “Since its debut, the group’s Telegram channels have been removed and recreated at least

Europol and Eurojust Dismantle €600 Million Crypto Fraud Network in Global Sweep

Nine people have been arrested in connection with a coordinated law enforcement operation that targeted a cryptocurrency money laundering network that defrauded victims of €600 million (~$688 million). According to a statement released by Eurojust today, the action took place