Fake Kling AI Facebook Ads Deliver RAT Malware to Over 22 Million Potential Victims

Counterfeit Facebook pages and sponsored ads on the social media platform are being employed to direct users to fake websites masquerading as Kling AI with the goal of tricking victims into downloading malware. Kling AI is an artificial intelligence (AI)-powered

Securing CI/CD workflows with Wazuh

Continuous Integration and Continuous Delivery/Deployment (CI/CD) refers to practices that automate how code is developed and released to different environments. CI/CD pipelines are fundamental in modern software development, ensuring code is consistently tested, built, and deployed quickly and efficiently. While

How to Detect Phishing Attacks Faster: Tycoon2FA Example

It takes just one email to compromise an entire system. A single well-crafted message can bypass filters, trick employees, and give attackers the access they need. Left undetected, these threats can lead to credential theft, unauthorized access, and even full-scale

Researchers Expose PWA JavaScript Attack That Redirects Users to Adult Scam Apps

Cybersecurity researchers have discovered a new campaign that employs malicious JavaScript injections to redirect site visitors on mobile devices to a Chinese adult-content Progressive Web App (PWA) scam. “While the payload itself is nothing new (yet another adult gambling scam),

Google Chrome Can Now Auto-Change Compromised Passwords Using Its Built-In Manager

Google has announced a new feature in its Chrome browser that lets its built-in Password Manager automatically change a user’s password when it detects the credentials to be compromised. “When Chrome detects a compromised password during sign in, Google Password

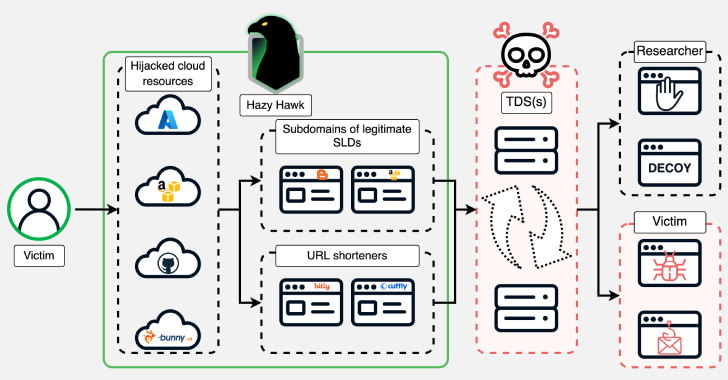
Hazy Hawk Exploits DNS Records to Hijack CDC, Corporate Domains for Malware Delivery

A threat actor known as Hazy Hawk has been observed hijacking abandoned cloud resources of high-profile organizations, including Amazon S3 buckets and Microsoft Azure endpoints, by leveraging misconfigurations in the Domain Name System (DNS) records. The hijacked domains are then

100+ Fake Chrome Extensions Found Hijacking Sessions, Stealing Credentials, Injecting Ads

An unknown threat actor has been attributed to creating several malicious Chrome Browser extensions since February 2024 that masquerade as seemingly benign utilities but incorporate covert functionality to exfiltrate data, receive commands, and execute arbitrary code. “The actor creates websites

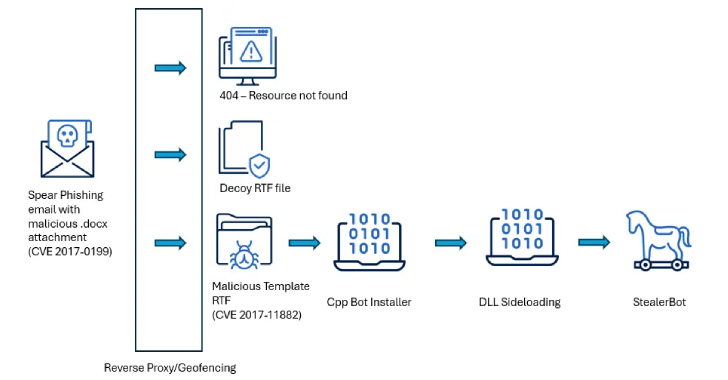
South Asian Ministries Hit by SideWinder APT Using Old Office Flaws and Custom Malware

High-level government institutions in Sri Lanka, Bangladesh, and Pakistan have emerged as the target of a new campaign orchestrated by a threat actor known as SideWinder. “The attackers used spear phishing emails paired with geofenced payloads to ensure that only

AWS Default IAM Roles Found to Enable Lateral Movement and Cross-Service Exploitation

Cybersecurity researchers have discovered risky default identity and access management (IAM) roles impacting Amazon Web Services that could open the door for attackers to escalate privileges, manipulate other AWS services, and, in some cases, even fully compromise AWS accounts. “These

The Crowded Battle: Key Insights from the 2025 State of Pentesting Report

In the newly released 2025 State of Pentesting Report, Pentera surveyed 500 CISOs from global enterprises (200 from within the USA) to understand the strategies, tactics, and tools they use to cope with the thousands of security alerts, the persisting