Newly SLEEPWALKER Backdoor Waits for One Crafted Packet, Then Runs Its Own Bytecode

An independent malware researcher has documented a previously unreported Windows backdoor, dubbed SLEEPWALKER, that stays inert in memory until a specifically crafted network packet reaches the machine and then runs commands written in a 23-instruction language of its own design.
Critical Gitea RCE Actively Exploited as Reported Attack Drops Miner-Like Payload

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday warned of active exploitation efforts targeting a recently patched critical security flaw impacting Gitea. The vulnerability in question is CVE-2026-60004 (CVSS score: 9.8), a case of remote code execution that

Fake Apple Support AI Calls Target Stolen-Device Owners for Passcodes and 2FA Codes

Cybersecurity researchers have disclosed details of a phishing-as-a-service (PhaaS) platform built to strip Apple’s Activation Lock from stolen devices, using rented AI voice agents that call theft victims posing as Apple Support and ask for their device passcode. SOCRadar Threat

U.S. Sanctions Iran-Linked Hackers Behind Critical Infrastructure Breaches

The U.S. Department of the Treasury has announced fresh sanctions on Iranian cyber actors as part of what it called an “unprecedented, whole-of-government, economic campaign” against the nation and its enablers. “We are launching an economic onslaught against Iran’s financial

A Malicious Webpage Could Poison Your Local AI Model Behind NVIDIA NemoClaw

Oasis Security has disclosed a weakness in NVIDIA NemoClaw that could let an attacker-controlled webpage take unauthenticated control of the local Ollama instance serving an AI agent and plant hidden instructions inside the model itself. The findings were shared with

WhatsApp Adds Multiple Passkeys for Phishing-Resistant Sign-Ins Across iOS and Android

Meta on Tuesday announced a set of WhatsApp account security features, including support for multiple passkeys to a single account to help users with both iOS and Android devices sign into their accounts using the phishing-resistant method. The tech giant

Marimo Notebook Flaw Could Run MCP Commands Before Cells Execute in Edit Mode

Marimo has addressed a high-severity security flaw in its notebook software that allowed an attacker to execute an attacker-supplied Model Context Protocol (MCP) command in a specially crafted notebook, according to VulnCheck’s CVE Numbering Authority (CNA) record. The CNA record

Mirage2FA Surge Hits 4,500 US and EU Companies, Abusing Microsoft 365 Login Flows

Thousands of companies have been affected by the Mirage2FA campaign from 2024 to 2026. The commercial phishing-as-a-service toolkit targets Microsoft 365 accounts by abusing legitimate login flows and bypassing two-factor authentication. According to ANY.RUN research, 48% of targeted email addresses

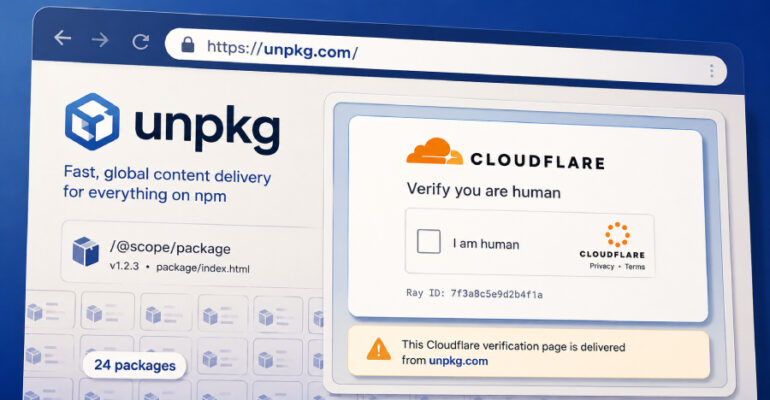
24 npm Packages Abuse unpkg Mirrors to Host Fake Cloudflare CAPTCHA Pages

Cybersecurity researchers have disclosed details of a new campaign that uses a cluster of 24 npm packages as free phishing infrastructure for redirecting to ClickFix-style fake CAPTCHA pages. “While the malware is simply a single HTML page inside the npm

E4del and PINHOLE RATs Turn FTP Banners Into Dead Drops for Malware Commands

Cybersecurity researchers are calling attention to a new campaign that employs FTP banners as dead drop resolvers (DDRs) to deliver two previously unreported remote access trojans (RATs) tracked as E4del and PINHOLE. While threat actors are known to abuse legitimate