Researchers Uncover Flaws in Popular Open-Source Machine Learning Frameworks

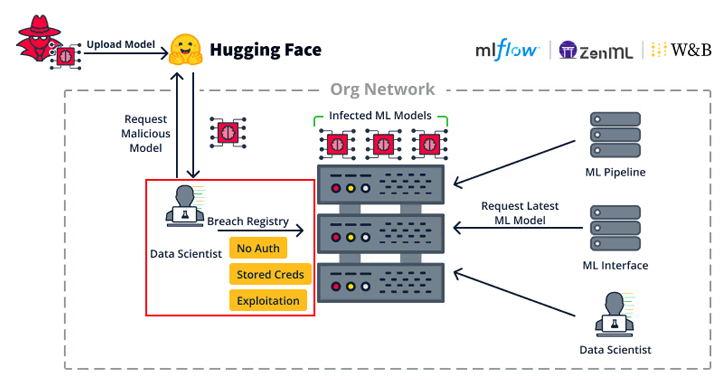
Cybersecurity researchers have disclosed multiple security flaws impacting open-source machine learning (ML) tools and frameworks such as MLflow, H2O, PyTorch, and MLeap that could pave the way for code execution. The vulnerabilities, discovered by JFrog, are part of a broader
Conquering the Complexities of Modern BCDR

The modern business landscape is thrilling yet daunting. Rapidly evolving technology, persistent cyberthreats and escalating operational complexities make data protection and seamless business continuity challenging for businesses of all sizes. Your organization needs robust security measures that go beyond traditional

More_eggs MaaS Expands Operations with RevC2 Backdoor and Venom Loader

The threat actors behind the More_eggs malware have been linked to two new malware families, indicating an expansion of its malware-as-a-service (MaaS) operation. This includes a novel information-stealing backdoor called RevC2 and a loader codenamed Venom Loader, both of which

Hackers Leveraging Cloudflare Tunnels, DNS Fast-Flux to Hide GammaDrop Malware

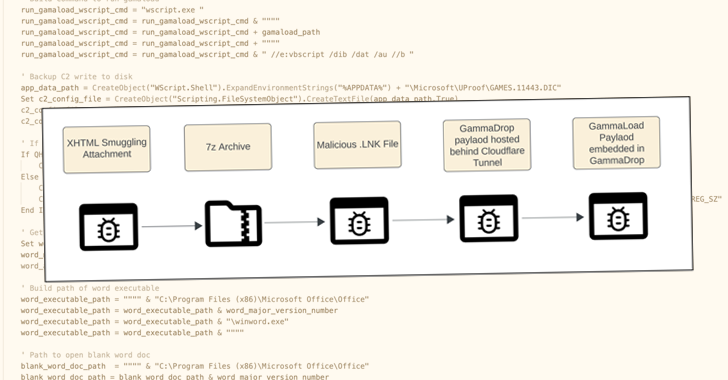
The threat actor known as Gamaredon has been observed leveraging Cloudflare Tunnels as a tactic to conceal its staging infrastructure hosting a malware called GammaDrop. The activity is part of an ongoing spear-phishing campaign targeting Ukrainian entities since at least

This $3,000 Android Trojan Targeting Banks and Cryptocurrency Exchanges

As many as 77 banking institutions, cryptocurrency exchanges, and national organizations have become the target of a newly discovered Android remote access trojan (RAT) called DroidBot. “DroidBot is a modern RAT that combines hidden VNC and overlay attack techniques with

Critical Mitel MiCollab Flaw Exposes Systems to Unauthorized File and Admin Access

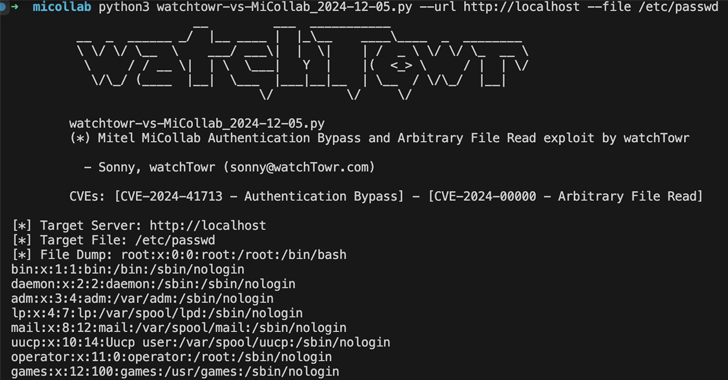
Cybersecurity researchers have released a proof-of-concept (PoC) exploit that strings together a now-patched critical security flaw impacting Mitel MiCollab with an arbitrary file read zero-day, granting an attacker the ability to access files from susceptible instances. The critical vulnerability in

Europol Shuts Down Manson Market Fraud Marketplace, Seizes 50 Servers

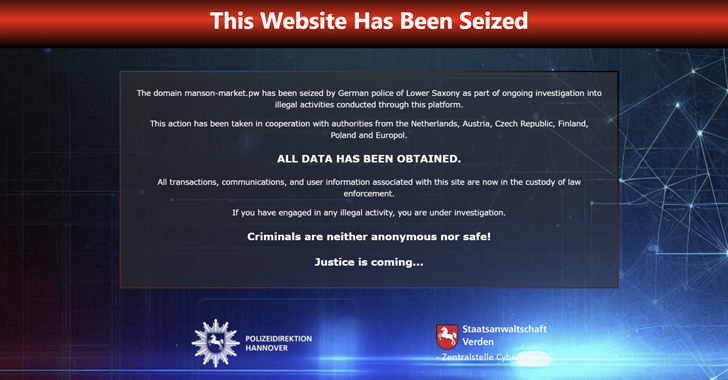
Europol on Thursday announced the shutdown of a clearnet marketplace called Manson Market that facilitated online fraud on a large scale. The operation, led by German authorities, has resulted in the seizure of more than 50 servers associated with the

Hackers Target Uyghurs and Tibetans with MOONSHINE Exploit and DarkNimbus Backdoor

A previously undocumented threat activity cluster dubbed Earth Minotaur is leveraging the MOONSHINE exploit kit and an unreported Android-cum-Windows backdoor called DarkNimbus to facilitate long-term surveillance operations targeting Tibetans and Uyghurs. “Earth Minotaur uses MOONSHINE to deliver the DarkNimbus backdoor

Want to Grow Vulnerability Management into Exposure Management? Start Here!

Vulnerability Management (VM) has long been a cornerstone of organizational cybersecurity. Nearly as old as the discipline of cybersecurity itself, it aims to help organizations identify and address potential security issues before they become serious problems. Yet, in recent years,

Researchers Uncover 4-Month Cyberattack on U.S. Firm Linked to Chinese Hackers

A suspected Chinese threat actor targeted a large U.S. organization earlier this year as part of a four-month-long intrusion. According to Broadcom-owned Symantec, the first evidence of the malicious activity was detected on April 11, 2024 and continued until August.