Researchers Uncover TLS Bootstrap Attack on Azure Kubernetes Clusters

Cybersecurity researchers have disclosed a security flaw impacting Microsoft Azure Kubernetes Services that, if successfully exploited, could allow an attacker to escalate their privileges and access credentials for services used by the cluster. “An attacker with command execution in a
Iranian Cyber Group TA453 Targets Jewish Leader with New AnvilEcho Malware

Iranian state-sponsored threat actors have been observed orchestrating spear-phishing campaigns targeting a prominent Jewish figure starting in late July 2024 with the goal of delivering a new intelligence-gathering tool called AnvilEcho. Enterprise security company Proofpoint is tracking the activity under

Blind Eagle Hackers Exploit Spear-Phishing to Deploy RATs in Latin America

Cybersecurity researchers have shed light on a threat actor known as Blind Eagle that has persistently targeted entities and individuals in Colombia, Ecuador, Chile, Panama, and other Latin American nations. Targets of these attacks span several sectors, including governmental institutions,

Thousands of Oracle NetSuite Sites at Risk of Exposing Customer Information

Cybersecurity researchers are warning about the discovery of thousands of externally-facing Oracle NetSuite e-commerce sites that have been found susceptible to leaking sensitive customer information. “A potential issue in NetSuite’s SuiteCommerce platform could allow attackers to access sensitive data due

CISA Warns of Critical Jenkins Vulnerability Exploited in Ransomware Attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical security flaw impacting Jenkins to its Known Exploited Vulnerabilities (KEV) catalog, following its exploitation in ransomware attacks. The vulnerability, tracked as CVE-2024-23897 (CVSS score: 9.8), is a path

New UULoader Malware Distributes Gh0st RAT and Mimikatz in East Asia

A new type of malware called UULoader is being used by threat actors to deliver next-stage payloads like Gh0st RAT and Mimikatz. The Cyberint Research Team, which discovered the malware, said it’s distributed in the form of malicious installers for

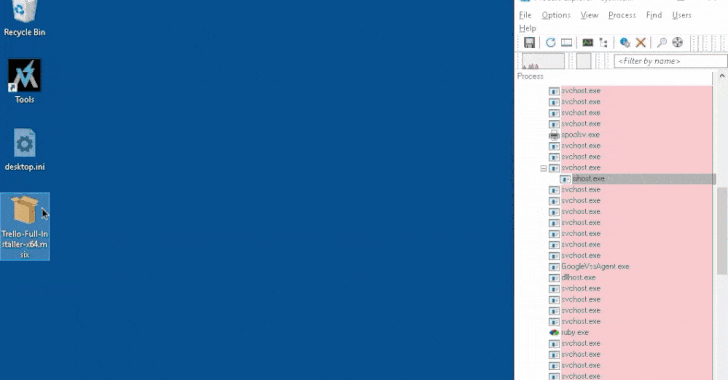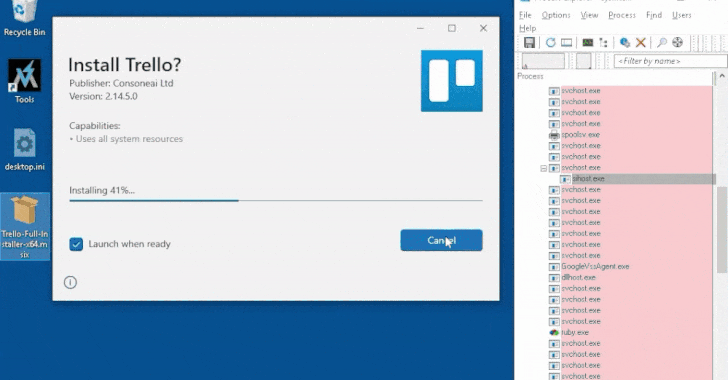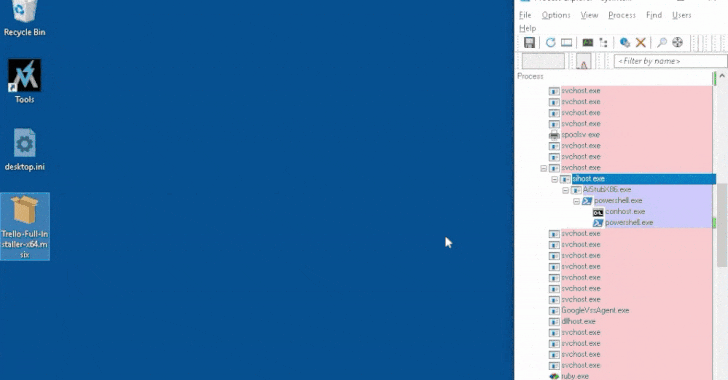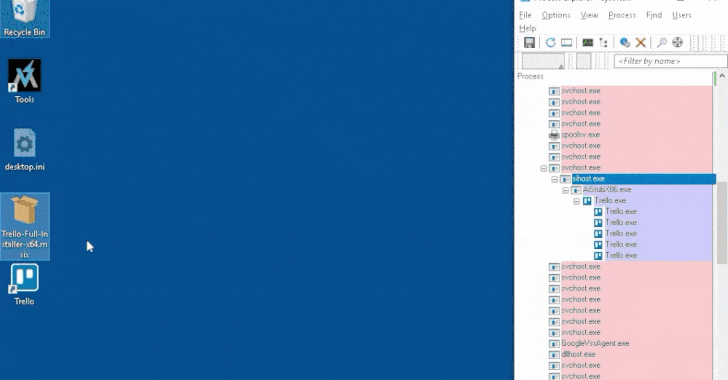
Cybercriminals Exploit Popular Software Searches to Spread FakeBat Malware

Cybersecurity researchers have uncovered a surge in malware infections stemming from malvertising campaigns distributing a loader called FakeBat. “These attacks are opportunistic in nature, targeting users seeking popular business software,” the Mandiant Managed Defense team said in a technical report.

How to Automate the Hardest Parts of Employee Offboarding

According to recent research on employee offboarding, 70% of IT professionals say they’ve experienced the negative effects of incomplete IT offboarding, whether in the form of a security incident tied to an account that wasn’t deprovisioned, a surprise bill for resources

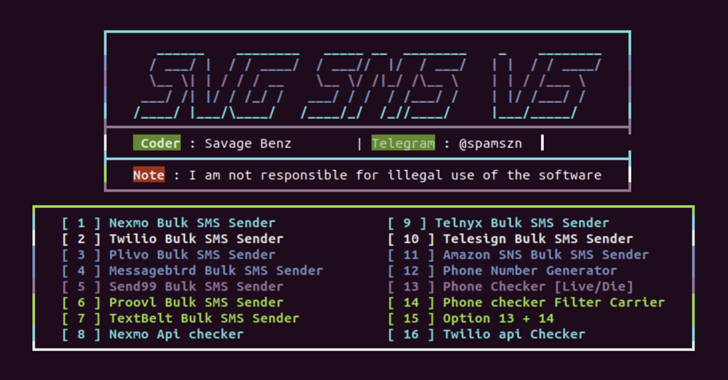
Xeon Sender Tool Exploits Cloud APIs for Large-Scale SMS Phishing Attacks

Malicious actors are using a cloud attack tool named Xeon Sender to conduct SMS phishing and spam campaigns on a large scale by abusing legitimate services. “Attackers can use Xeon to send messages through multiple software-as-a-service (SaaS) providers using valid

Microsoft Patches Zero-Day Flaw Exploited by North Korea’s Lazarus Group

A newly patched security flaw in Microsoft Windows was exploited as a zero-day by Lazarus Group, a prolific state-sponsored actor affiliated with North Korea. The security vulnerability, tracked as CVE-2024-38193 (CVSS score: 7.8), has been described as a privilege escalation