CrowdStrike Reveals Root Cause of Global System Outages

Cybersecurity company CrowdStrike has published its root cause analysis detailing the Falcon Sensor software update crash that crippled millions of Windows devices globally. The “Channel File 291” incident, as originally highlighted in its Preliminary Post Incident Review (PIR), has been
Chameleon Android Banking Trojan Targets Users Through Fake CRM App

Cybersecurity researchers have lifted the lid on a new technique adopted by threat actors behind the Chameleon Android banking trojan targeting users in Canada by masquerading as a Customer Relationship Management (CRM) app. “Chameleon was seen masquerading as a CRM

Apple’s New macOS Sequoia Tightens Gatekeeper Controls to Block Unauthorized Software

Apple on Tuesday announced an update to its next-generation macOS version that makes it a little more difficult for users to override Gatekeeper protections. Gatekeeper is a crucial line of defense built into macOS designed to ensure that only trusted

INTERPOL Recovers $41 Million in Largest Ever BEC Scam in Singapore

INTERPOL said it devised a “global stop-payment mechanism” that helped facilitate the largest-ever recovery of funds defrauded in a business email compromise (BEC) scam.  The development comes after an unnamed commodity firm based in Singapore fell victim to a BEC

Suspicious Minds: Insider Threats in The SaaS World

Everyone loves the double-agent plot twist in a spy movie, but it’s a different story when it comes to securing company data. Whether intentional or unintentional, insider threats are a legitimate concern. According to CSA research, 26% of companies who

North Korean Hackers Moonstone Sleet Push Malicious JS Packages to npm Registry

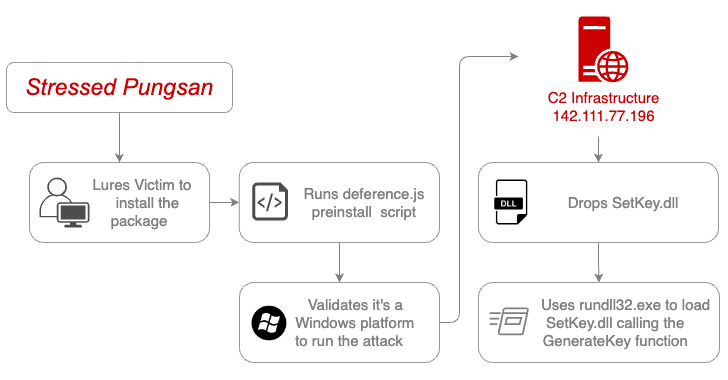
The North Korea-linked threat actor known as Moonstone Sleet has continued to push malicious npm packages to the JavaScript package registry with the aim of infecting Windows systems, underscoring the persistent nature of their campaigns. The packages in question, harthat-api

New Android Spyware LianSpy Evades Detection Using Yandex Cloud

Users in Russia have been the target of a previously undocumented Android post-compromise spyware called LianSpy since at least 2021. Cybersecurity vendor Kaspersky, which discovered the malware in March 2024, noted its use of Yandex Cloud, a Russian cloud service,

Google Patches New Android Kernel Vulnerability Exploited in the Wild

Google has addressed a high-severity security flaw impacting the Android kernel that it has been actively exploited in the wild. The vulnerability, tracked as CVE-2024-36971, has been described as a case of remote code execution impacting the kernel. “There are

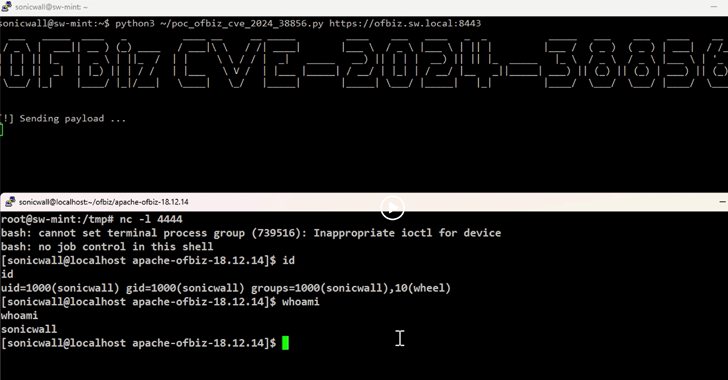
New Zero-Day Flaw in Apache OFBiz ERP Allows Remote Code Execution

A new zero-day pre-authentication remote code execution vulnerability has been disclosed in the Apache OFBiz open-source enterprise resource planning (ERP) system that could allow threat actors to achieve remote code execution on affected instances. Tracked as CVE-2024-38856, the flaw has

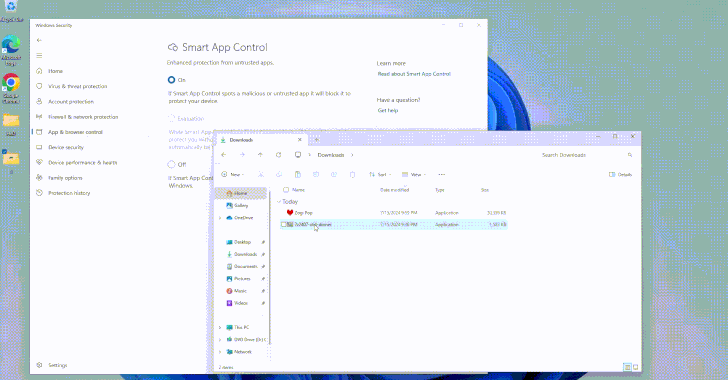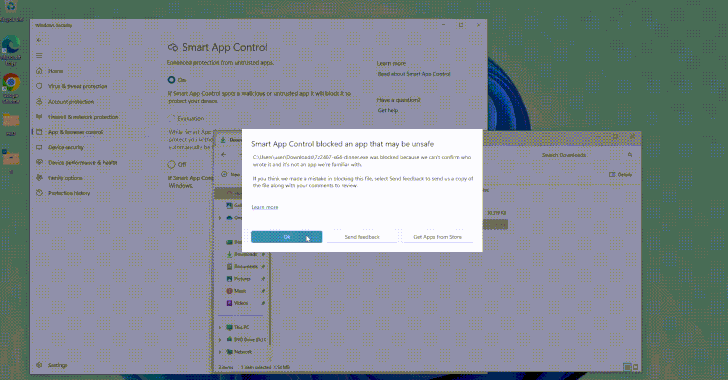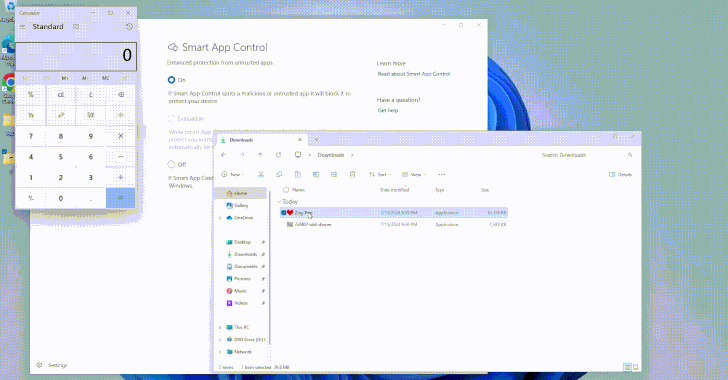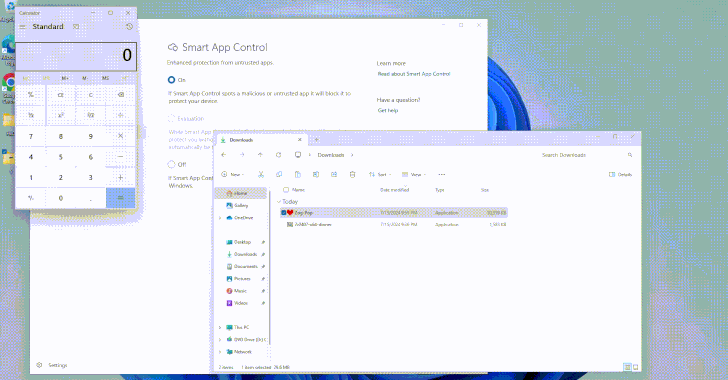
Researchers Uncover Flaws in Windows Smart App Control and SmartScreen

Cybersecurity researchers have uncovered design weaknesses in Microsoft’s Windows Smart App Control and SmartScreen that could enable threat actors to gain initial access to target environments without raising any warnings. Smart App Control (SAC) is a cloud-powered security feature introduced