Webinar: Discover the All-in-One Cybersecurity Solution for SMBs

In today’s digital battlefield, small and medium businesses (SMBs) face the same cyber threats as large corporations, but with fewer resources. Managed service providers (MSPs) are struggling to keep up with the demand for protection. If your current cybersecurity strategy
Mirai Botnet targeting OFBiz Servers Vulnerable to Directory Traversal

Enterprise Resource Planning (ERP) Software is at the heart of many enterprising supporting human resources, accounting, shipping, and manufacturing. These systems can become very complex and difficult to maintain. They are often highly customized, which can make patching difficult. However,

New Windows Backdoor BITSLOTH Exploits BITS for Stealthy Communication

Cybersecurity researchers have discovered a previously undocumented Windows backdoor that leverages a built-in feature called Background Intelligent Transfer Service (BITS) as a command-and-control (C2) mechanism. The newly identified malware strain has been codenamed BITSLOTH by Elastic Security Labs, which made

U.S. Releases High-Profile Russian Hackers in Diplomatic Prisoner Exchange

In a historic prisoner exchange between Belarus, Germany, Norway, Russia, Slovenia, and the U.S., two Russian nationals serving time for cybercrime activities have been freed and repatriated to their country. This includes Roman Valerevich Seleznev and Vladislav Klyushin, who are

Cybercriminals Abusing Cloudflare Tunnels to Evade Detection and Spread Malware

Cybersecurity companies are warning about an uptick in the abuse of Clouflare’s TryCloudflare free service for malware delivery. The activity, documented by both eSentire and Proofpoint, entails the use of TryCloudflare to create a one-time tunnel that acts as a

Over 1 Million Domains at Risk of ‘Sitting Ducks’ Domain Hijacking Technique

Over a million domains are susceptible to takeover by malicious actors by means of what has been called a Sitting Ducks attack. The powerful attack vector, which exploits weaknesses in the domain name system (DNS), is being exploited by over

Hackers Distributing Malicious Python Packages via Popular Developer Q&A Platform

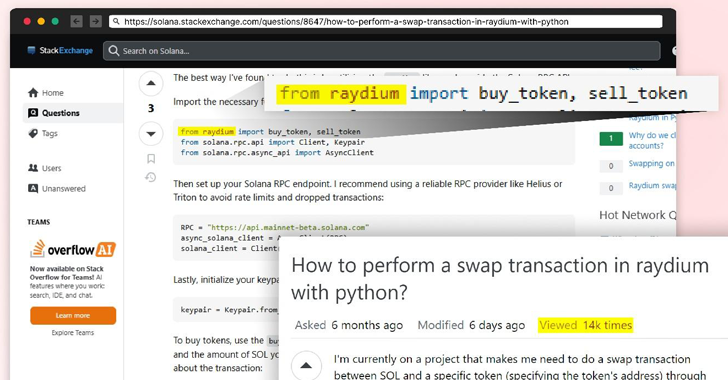
In yet another sign that threat actors are always looking out for new ways to trick users into downloading malware, it has come to light that the question-and-answer (Q&A) platform known as Stack Exchange has been abused to direct unsuspecting

New Android Banking Trojan BingoMod Steals Money, Wipes Devices

Cybersecurity researchers have uncovered a new Android remote access trojan (RAT) called BingoMod that not only performs fraudulent money transfers from the compromised devices but also wipes them in an attempt to erase traces of the malware. Italian cybersecurity firm

Obfuscation: There Are Two Sides To Everything

How to detect and prevent attackers from using these various techniques Obfuscation is an important technique for protecting software that also carries risks, especially when used by malware authors. In this article, we examine obfuscation, its effects, and responses to

Google Chrome Adds App-Bound Encryption to Protect Cookies from Malware

Google has announced that it’s adding a new layer of protection to its Chrome browser through what’s called app-bound encryption to prevent information-stealing malware from grabbing cookies on Windows systems. “On Windows, Chrome uses the Data Protection API (DPAPI) which