Attackers Exploit ‘Ill Bloom’ Vulnerability to Drain $3.1 Million From Cryptocurrency Wallets

Security firm Coinspect has disclosed a crypto wallet flaw it calls Ill Bloom, and attackers are already using it. The flaw is in how some wallet software generated its recovery phrase, the words that control the money. When that phrase is made with

Ransomware Negotiator Gets 70 Months in Prison for Aiding BlackCat Attacks

A 41-year-old former ransomware negotiator has been sentenced to nearly six years (i.e., 70 months) in prison in the U.S. for their role in conspiring with the now-defunct BlackCat ransomware operators to extort multiple victims and working with two other

Dormant GitHub Accounts Help Attackers Blend In While Mapping Corporate Orgs

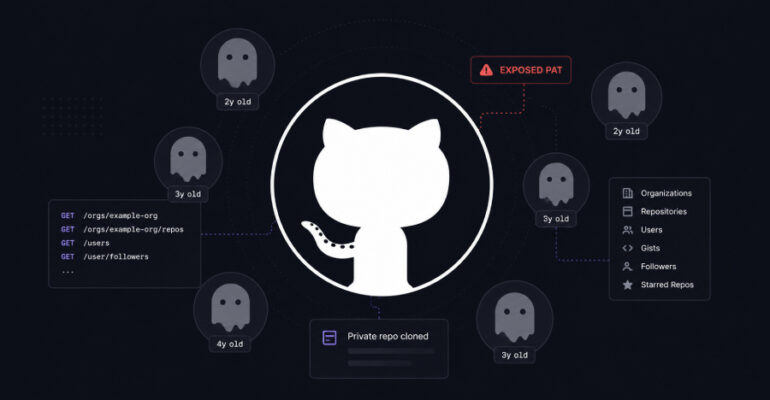
Datadog Security Labs is warning of “several overlapping campaigns” that are systematically enumerating corporate GitHub organizations, repositories, and user accounts through the GitHub API. “Operators rely on automated scraping tooling with custom or legitimate-sounding user agents, leveraging GitHub ‘ghost’ accounts that

New GigaWiper Windows Backdoor Bundles Disk Wiping, Fake Ransomware, and Spyware

Microsoft has taken apart a destructive Windows backdoor it calls GigaWiper. What stands out is how it is built: not one tool but three older destructive programs bolted into one, offered as commands the operator can choose from. Each is

npm 12 Disables Install Scripts by Default to Reduce Supply Chain Risk

GitHub has officially announced the release of npm version 12 with install scripts disabled by default, along with deprecating granular access tokens (GATs) designed to bypass two-factor authentication (2FA). The Microsoft-owned subsidiary noted that the following npm install behaviors that

ThreatsDay: Cloud Bucket Hijacking, Windows LPE Chain, Global Fraud Bust + 17 More Stories

Most security mess starts as admin work. A link gets clicked. A tool gets trusted. A bucket name gets reused. A setting stays loose because nobody wants to touch it. This week is full of that kind of damage. Not loud.

AI Attacks Move in Minutes. Join This Webinar on Building a Defense That Keeps Up

AI has changed how fast attacks move. Work that once took an attacker days now takes minutes. Using models like Mythos, attackers write tailored bait, pick targets, test what lands, and jump to the next host before your team clears

Summer of Clearinghouses

Everyone seems to have announced a clearinghouse over the past few weeks. We did too. Ours is called Athena, and the main thing that sets it apart is that it was already real and running when we announced it —

GodDamn Ransomware Uses PoisonX Driver to Disable Endpoint Defenses

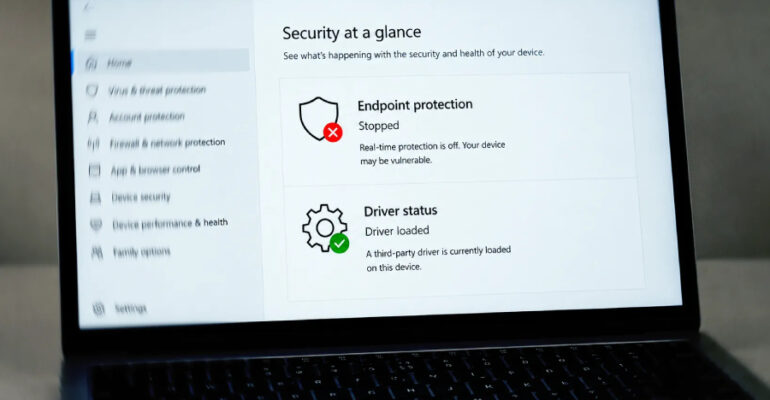
Cybersecurity researchers have flagged a new ransomware family called GodDamn that employs the PoisonX kernel driver to neutralize security software as part of its defense evasion strategy. According to a new report published by the Threat Hunter Team from Symantec,

Microsoft Patches RoguePlanet Defender Flaw That Can Grant SYSTEM Privileges

Microsoft has released security updates for a Defender vulnerability known as RoguePlanet, nearly a month after details of the flaw became public. The vulnerability, tracked as CVE-2026-50656 (CVSS score: 7.8), is a privilege escalation issue in the Microsoft Malware Protection