CISA Warns Fortinet Customers as FortiBleed Hits 86,644 FortiGate Devices

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday urged Fortinet customers with FortiGate appliances to take steps to secure against ongoing malicious activity aimed at thousands of internet-accessible devices. The sweeping campaign, believed to be the work of
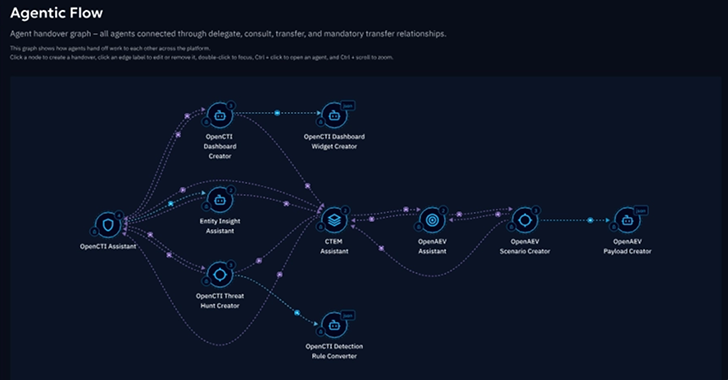
From Assistive to Agentic: The AI Shift That’s Redefining Threat Management

Introduction The average enterprise security team has 40 or more security tools, giving a lot of visibility into internal telemetry and asset data. But often, these tools are working in siloes, generating (overlapping) alerts and data. And yet, breach dwell

Forget Data Leakage: Shadow AI’s Real Threat Is Access Control

The first wave of enterprise AI concern was straightforward. It was simply employees pasting sensitive data into public AI tools. Security teams responded with usage policies, domain blocks, and data loss prevention rules. That response made sense at the time.

Salesforce Disables Klue App Integration After OAuth Token Abuse Exposes Customer Data

Salesforce has revealed that it disabled the Klue Battlecards app integration within its platform in response to a security incident impacting the competitive intelligence company on June 11, 2026. To that end, organizations will be unable to connect to Salesforce

Apple Patches Beats Studio Buds Flaw Letting Nearby Attackers Spy via Microphone

Apple has updated its Beats Studio Buds wireless earbuds to patch a high-severity vulnerability that could be exploited by nearby hackers to eavesdrop on users. The vulnerability, tracked as CVE-2025-20701 (CVSS score: 8.8), refers to a case of incorrect authorization

F5 Patches Two Critical NGINX Open Source Flaws Enabling Remote Code Execution

F5 has released security updates to address two critical security flaws in NGINX Open Source that could be exploited to achieve code execution on affected systems. The vulnerabilities are listed below – CVE-2026-42530 (CVSS v4 score: 9.2) – A use-after-free

ThreatsDay Bulletin: Claude Chat Abuse, NastyC2 npm Packages, Device-Code Phishing + 25 More Stories

The internet did not break this week. It got used exactly as designed, which is worse. Searches were siphoned through shady browser add-ons. AI chat links turned into malware delivery paths. macOS attacks ran in memory and left almost nothing

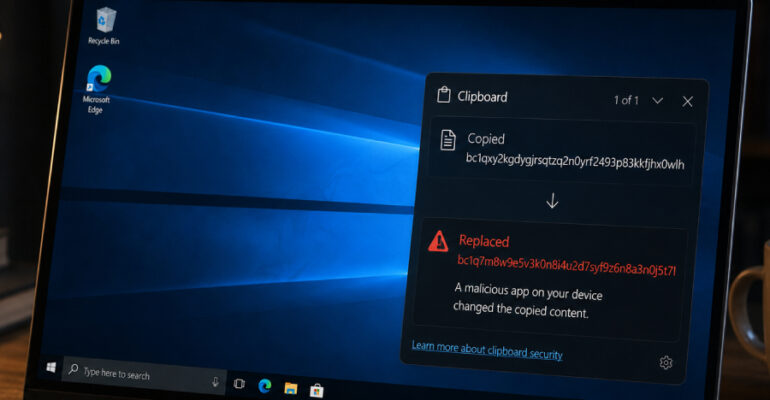
Microsoft Details Windows Clipper Malware Campaign Using USB LNK Worm and Tor-Based C2

Microsoft has disclosed details of a Windows-based cryptocurrency clipper campaign that has targeted users since February 2026. “The clipper in this campaign relies on Windows Script Host and ActiveX-driven logic to launch a bundled Tor proxy and poll a hidden-service

INC Ransomware Emerges as Major RaaS Threat in 2026 with 830+ Victims Since 2023

Cybersecurity researchers have charted the evolution of INC from an nascent ransomware-as-a-service (RaaS) operation to one of the most prolific cybercrime groups in 2026, claiming no less than 830 victims since August 2023. “The disruption of LockBit and the shutdown

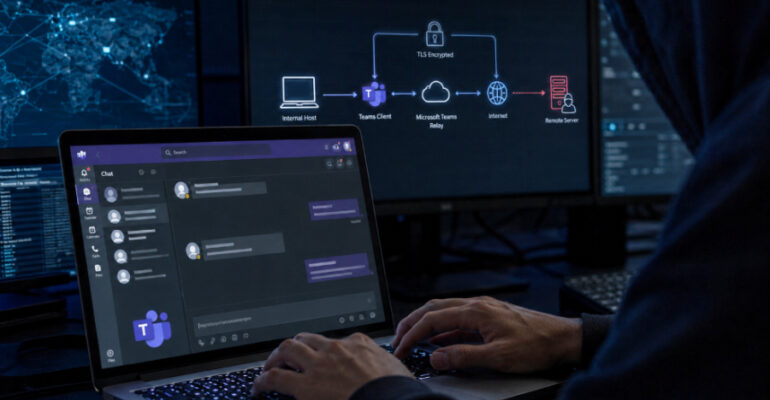
DragonForce Hackers Abuse Microsoft Teams Relays to Hide Backdoor.Turn C2 Traffic

Threat actors associated with the DragonForce ransomware have been observed using a custom Go-based remote access trojan (RAT) called Backdoor.Turn to conceal command-and-control (C2) traffic inside Microsoft Teams relay infrastructure. According to findings from Broadcom-owned Symantec and Carbon Black, the