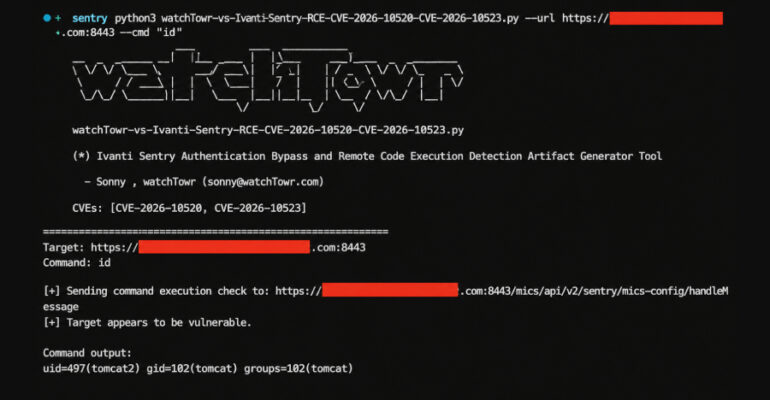
Ivanti, Fortinet, and SAP Release Patches for Multiple Critical Vulnerabilities

Fortinet, Ivanti, and SAP have released security updates to address multiple critical security vulnerabilities that could result in arbitrary code execution and information disclosure. The security flaw patched by Fortinet relates to a command injection vulnerability in FortiSandbox, FortiSandbox Cloud,
Unpatched Langflow Flaw CVE-2026-5027 Exploited for Unauthenticated RCE

A high-severity unpatched security flaw in Langflow, an open-source low-code platform to build artificial intelligence (AI) applications, has come under active exploitation in the wild, according to findings from VulnCheck. The vulnerability in question is CVE-2026-5027 (CVSS score: 8.8), a

CISA Adds Cisco, Chrome, and Arista Flaws to KEV Catalog Amid Active Exploitation

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added three new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The list of vulnerabilities is as follows – CVE-2026-20245 (CVSS score: 7.8) – An

Your Automated Pentest Looks Clean. See What It Missed in This Expert Webinar

Your pentest report looks clean. That might be the problem. Run automated pentesting long enough, and the new findings start to dry up. By the third or fourth run, fewer issues appear. The report looks stable. Leadership reads “stable” as

Microsoft Patches Record 206 Flaws, Including Three Zero-Days and Critical RCE Bugs

Microsoft on Tuesday released fixes for a record 206 security vulnerabilities impacting its software portfolio, including three flaws that have been publicly disclosed at the time of release. Of the 206 flaws, 39 are rated Critical, and 167 are rated

Anthropic Releases Claude Fable 5, Its Most Powerful AI Yet, With Cyber Safeguards

On June 9, Anthropic released Claude Fable 5, the most capable model it has ever made, generally available. It also did something unusual: it shipped one model as two products, split not by capability but by a layer of safety

ServiceNow Flaw Exploited to Gain Unauthorized Access to Customer Instances

ServiceNow has warned about a security incident in which unknown threat actors exploited a flaw to obtain deeper unauthorized access to susceptible instances. “On June 5, 2026, ServiceNow applied a security update to hosted customer instances,” the company revealed in

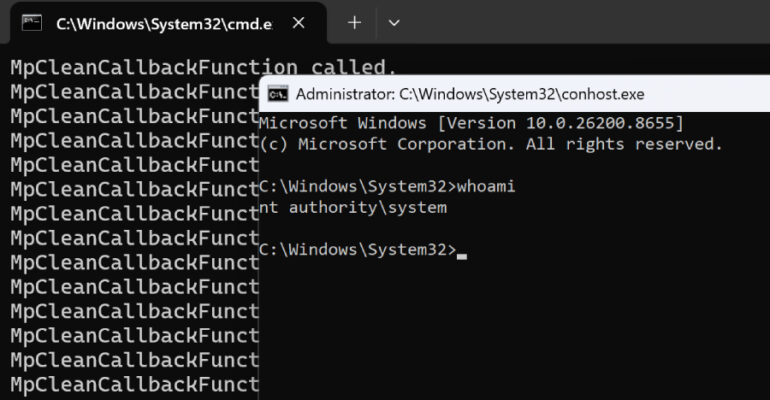
Microsoft Defender RoguePlanet Zero-Day Grants SYSTEM Access on Updated Windows

The anonymous security researcher going by the name Chaotic Eclipse (aka Nightmare-Eclipse) has released a proof-of-concept (PoC) exploit for yet another Microsoft Defender zero-day named RoguePlanet. “The exploit is a race condition, so it’s a hit or miss,” the researcher,

Six Proto6 Vulnerabilities in protobuf.js Expose Node.js Apps to RCE and DoS

Cybersecurity researchers have flagged half a dozen vulnerabilities in protobuf.js, a JavaScript and TypeScript implementation of Protocol Buffers (Protobuf), that, if successfully exploited, could result in remote code execution (RCE) and denial-of-service (DoS) attacks. “In affected environments, a single malicious

Meta to Use Off-Site Business Data for Feed and AI Personalization

Meta on Tuesday announced that it will use information shared by other businesses to personalize users’ feed and responses from its artificial intelligence (AI) chatbot, expanding its scope beyond targeted ads. “Businesses often share information about people’s activity on their