Keystone to Destroy 18,835 Hardware Wallets After Hackers Steal Device Verification Key

An attacker who gained access to Keystone’s website obtained the key that its hardware wallets use to prove they are genuine, the company said in a statement on October 26. Someone with that key could build counterfeit devices that pass the online
AI-Generated Fake Login Pages Are Making Account Takeovers Easier

Fake login pages are nothing new, but generative AI is making them easier to build and more convincing. Attackers can recreate familiar login screens, impersonate trusted brands and tailor phishing attempts to specific employees or organizations.  Some fake login pages

Lazarus Abuses South Korean Security Software to Deploy Malware Using Post-Quantum Encryption

The North Korea-linked Lazarus Group has been attributed to a cyber espionage campaign dubbed Operation FlashHole targeting at least three organizations in South Korea spanning the construction, software, and wire-communication equipment manufacturing sectors. According to Russian cybersecurity company Kaspersky, the

Australia Gets Into Amadey Malware Backend, Cuts Off Access to 180,000 Infected Computers

A criminal using the Amadey malware can no longer access or steal data from 180,000 infected computers around the world, including some in Australia, the Australian Signals Directorate (ASD) says. The agency’s operators gained access to the criminal’s operation’s backend

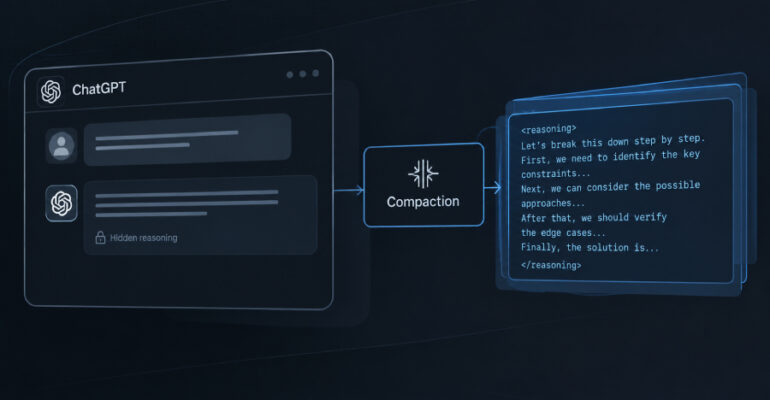
OpenAI Compaction Flaw Let Researchers Bypass Hidden Reasoning Protections

OpenAI’s compaction feature, which shrinks a long conversation to save space, could be turned into a way to copy a model’s hidden reasoning out in plain text, security firm Xint has shown. OpenAI’s reasoning models work through a problem before answering, and

Attackers Hijack Dahua IP Cameras in Ukraine Using P2P Access and Auth Weaknesses

The Computer Emergency Response Team of Ukraine (CERT-UA) has issued an alert warning of unauthorized remote access to video surveillance systems manufactured by Dahua. “Cases of compromising IP cameras and DVRs with access to the video stream, changing the device

CISA Confirms Active Exploitation of Two PHP2Shell Flaws Enabling Remote Code Execution

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday confirmed active exploitation of the recently patched PHP2Shell flaws by adding them to its Known Exploited Vulnerabilities (KEV) catalog. The PHP vulnerabilities, both rated 9.2 on the CVSS scoring system,

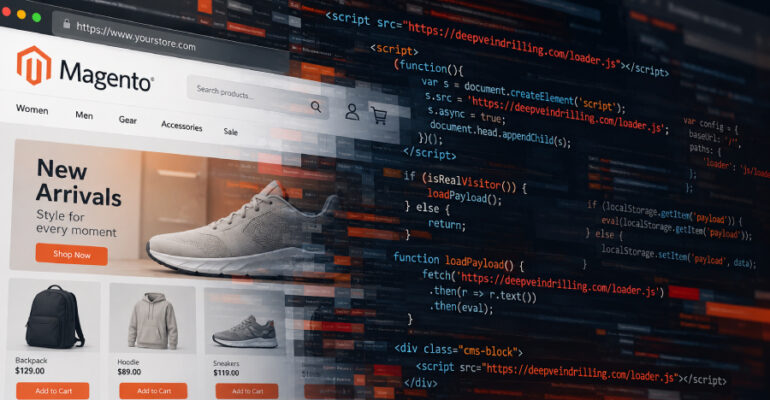
Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento

An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025. According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece

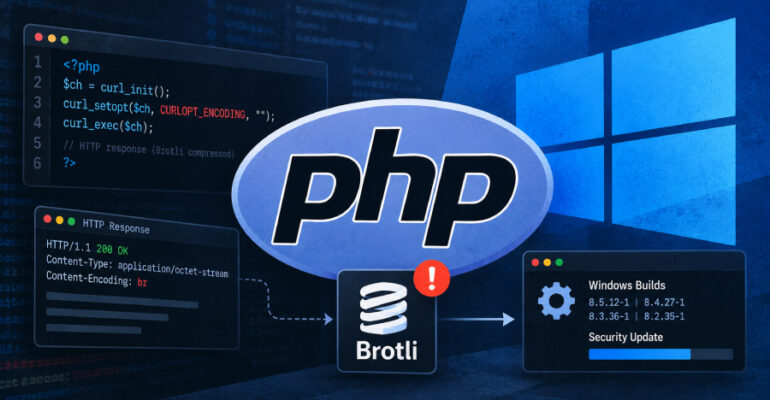
PHP Issues Second Windows Security Update in Five Days to Fix Brotli Code Execution Flaw

PHP has rebuilt its official Windows packages for PHP 8.2 through 8.5 to fix CVE-2026-111497, a flaw in the Brotli compression library that the packages include. The flaw can let an attacker corrupt memory and potentially run code. PHP says

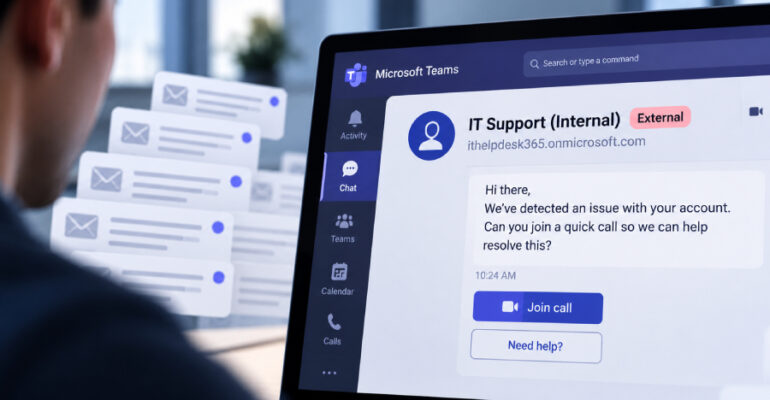
Attackers Use Microsoft Teams IT Support Scams to Deploy Malware and Ransomware

Cybersecurity researchers are calling attention to what they say is a “recurring social engineering pattern” across hundreds of cases in which threat actors use Microsoft Teams’ external chat creation feature to conduct impersonation scams or to deliver malware. “A consistent