Meta Blocks NSO Group’s New WhatsApp Phishing Attack, Files Contempt Order

Meta on Monday said it detected and blocked spear-phishing attempts linked to Israeli spyware vendor NSO Group. In addition, the tech giant said it’s filing a federal court contempt order against the company for violating a permanent injunction that barred
Critical Check Point VPN Flaw Exploited to Bypass Passwords in IKEv1 Setups

Check Point has warned of active exploitation of a critical vulnerability impacting Remote Access VPN and Mobile Access deployments that are configured to use the deprecated IKEv1 key exchange protocol. The vulnerability, tracked as CVE-2026-50751 (CVSS score: 9.3), is a

⚡ Weekly Recap: Instagram Account Hacks, Android Zero-Day, GitHub Worm and More

Monday again. The weekend was meant to be quiet. It wasn’t. Last week had poisoned packages, a broken AI helper, and a worm tearing through repos. The ugly part: basic tricks still worked. A chatbot got fooled. A bot token

AI Phishing Is Crushing SOCs with Alert Volume: How to Reduce Tier 1 Overload

Phishing has always been a numbers game. AI has turned it into a volume machine. Attackers can now create convincing emails, fake login pages, and tailored lures in minutes. Every polished message adds another case for Tier 1 to review,

The Hardest Fork

Mythos is real. I know a big chunk of the industry thinks it’s a marketing stunt, and I get why. I get it. But I’ve seen the findings, and they’re bad. These aren’t “whoops, this line right here is wrong,

VerdantBamboo Deploys BSD Variant of BRICKSTORM on Linux Appliances

A China-nexus cyber espionage group has been observed deploying a BSD variant of a known backdoor called BRICKSTORM, as well as two other malware families codenamed PLENET (aka GRIMBOLT) and AGENTPSD to target Linux systems. The activity has been attributed

UNC3753 Used Vishing and Physical Intrusions in U.S. Data Theft Extortion Campaign

Cybersecurity researchers have disclosed details of a financially motivated data theft extortion campaign that has targeted dozens of organizations across professional, legal, and financial services in the U.S. between January and May 2026. The activity has been attributed by Google

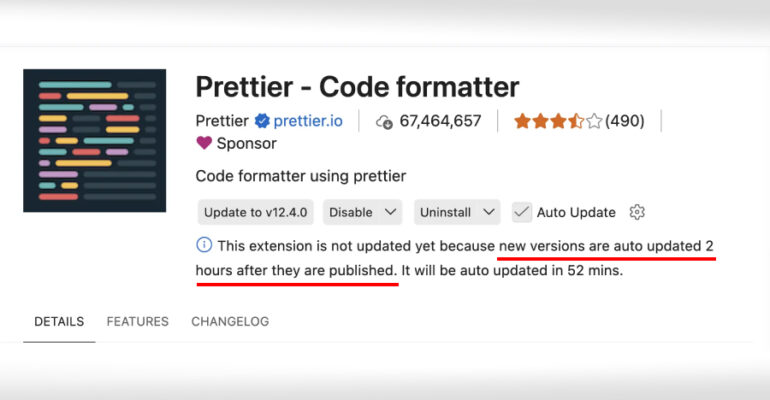
VS Code Adds 2-Hour Extension Auto-Update Delay to Limit Supply Chain Attacks

Microsoft has announced that Visual Studio Code (VS Code) will apply a two-hour delay before extensions for the integrated development environment (IDE) are updated automatically to a newer version in an attempt to tackle software supply chain threats. “When automatic

New ChatGPT Lockdown Mode Limits Tools That Could Enable Data Exfiltration

OpenAI has begun rolling out a new Lockdown Mode to ChatGPT for eligible personal accounts to reduce the risk of data exfiltration arising from prompt injection attacks. The feature is primarily designed for people and organizations that handle sensitive data

Free Apps Are Quietly Turning Smart TVs Into Web-Scraping Proxies for AI

A researcher has reverse-engineered the iOS SDK that Bright Data embeds in consumer apps and documented how it turns devices, including always-on smart TVs, into exit nodes that relay web-scraping traffic for a data business Bright Data markets heavily to