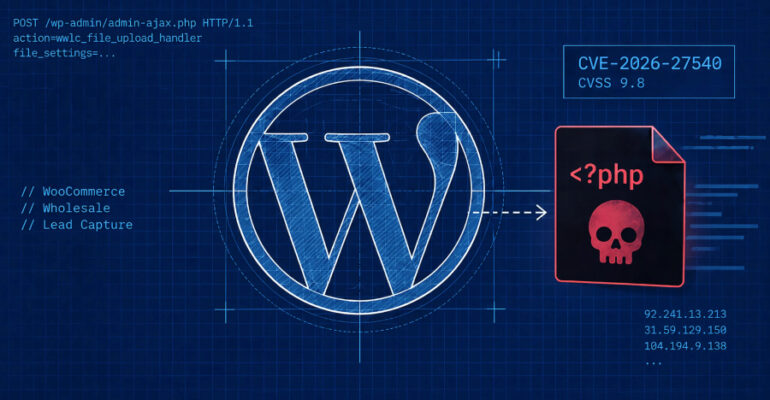
Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. “This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and