
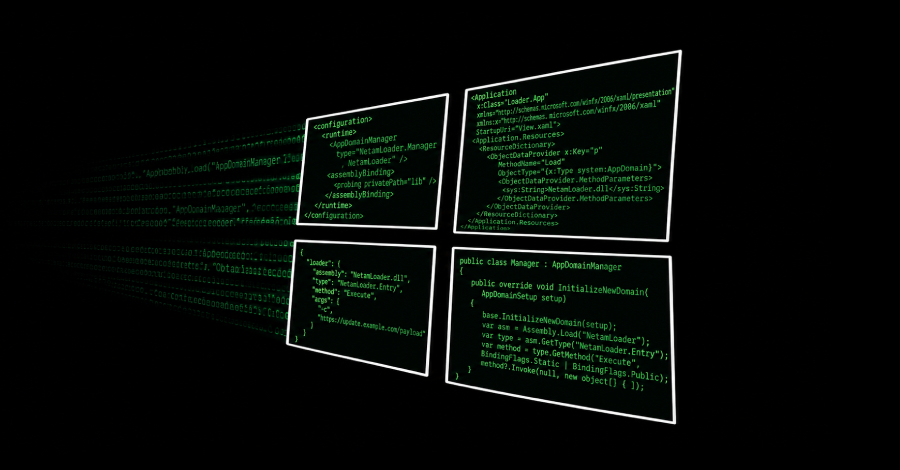
Cybersecurity researchers have disclosed details of what has been described as a “highly sophisticated infection chain” targeting government organizations in Asia.
The activity, detailed by Kaspersky this week, targeted a custom Windows 10 build used exclusively by government entities in Asia and involves the deployment of a previously undocumented .NET assembly-loading framework codenamed…
Read the rest of the story at Read More
Source: The Hacker News
Recent News


Leave a Comment