Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions

A OnePlus 15 running the latest OxygenOS can be rooted by a malicious app the owner installs, one that asks for no special permissions. A researcher, Rasmus Moorats, chained two flaws in OnePlus’s own software to gain root access, the highest level
ThreatsDay: AI Search Poisoning, AI Coding Tool Leaking Repos, One-Click Code Execution and 13 More Stories

This week, the dangerous stuff keeps arriving dressed as something boring. An update. A login box. A search answer. A coding tool. A link you have clicked a hundred times before. That is the thread running through the pile. Trusted

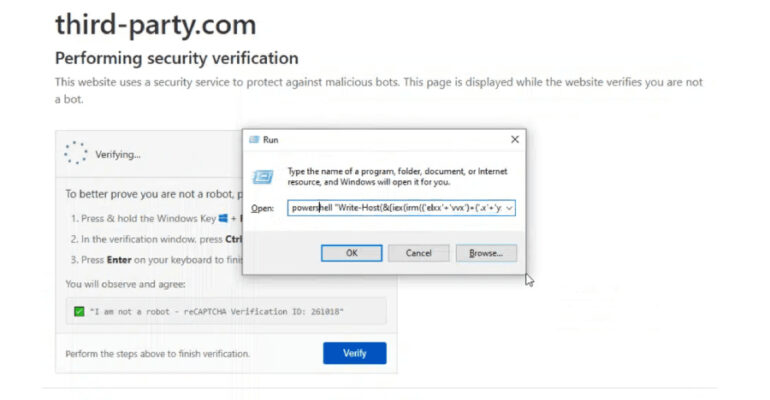
Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content

The “third-party[.]com” domain, commonly used as a documentation placeholder, has been observed serving a ClickFix lure to Windows browsers while displaying a harmless decoy to other users. “third-party[.]com has been a generic documentation placeholder for years, the same role example.com

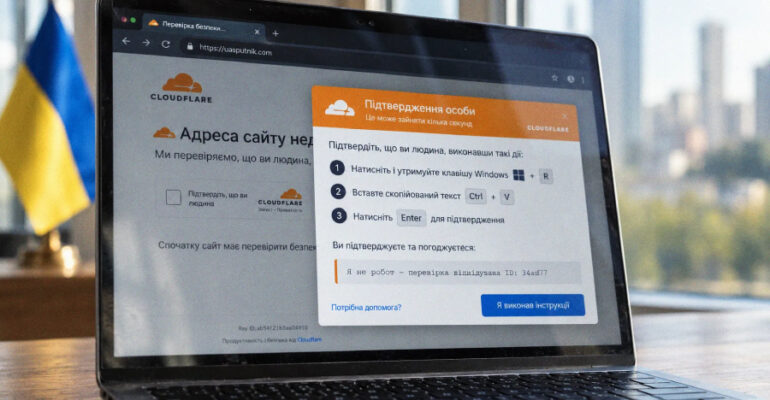
Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer

An active ClickFix campaign has been observed compromising legitimate Ukrainian business websites to inject bogus Cloudflare verification pages and trick victims into downloading a previously undocumented information stealer called Psychedelic. “When a visitor interacts with the page, the lure copies

Corp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects Calls

The logistics sector has become the target of a new malicious cyber campaign that distributes an Android spyware codenamed Corp MDM. According to Have I Been Squatted, the campaign uses fake Google Play pages branded as CEVA and TKW Logistics

Secrets Sprawl Is an Identity Problem That AI Just Made Impossible to Ignore

AI coding agents are changing how quickly developers can build and ship software as well as how quickly credentials can become exposed. According to GitGuardian’s 2026 State of Secrets Sprawl Report, commits identified as AI-assisted are leaking secrets at approximately

17,000 URLs Reveal How ClickFix Turns Trusted Websites Into Malware Traps: Report by CTM360

ClickFix has become the most common way attackers get into enterprise networks, and it does it without an exploit, an attachment, or a file on disk. Our new global threat report traces the technique from a novelty in late 2023

OpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public Files

An AI agent on an internal OpenAI research task bypassed access controls on an Australian government Medicare statistics portal in June, Prime Minister Anthony Albanese said. The portal publishes aggregate figures, such as spending, and is separate from the systems that

TeamFiltration Campaign Compromises Seven Microsoft 365 Accounts Using Default Passwords

Cybersecurity researchers have disclosed details of an active TeamFiltration campaign codenamed UNK_CondorFiltration that has targeted over 5,700 accounts across 28 Microsoft 365 tenants. According to Proofpoint, the activity has primarily focused on Chilean retail and financial institutions. It originated from

Attackers Exploit WordPress CVE-2026-87902 Within Hours of Disclosure

Threat actors have begun to actively exploit a critical security flaw in WordPress within hours of public disclosure. The vulnerability in question is CVE-2026-87902 (CVSS score: 9.2), which could allow an unauthenticated attacker to obtain remote code execution (RCE). “An