





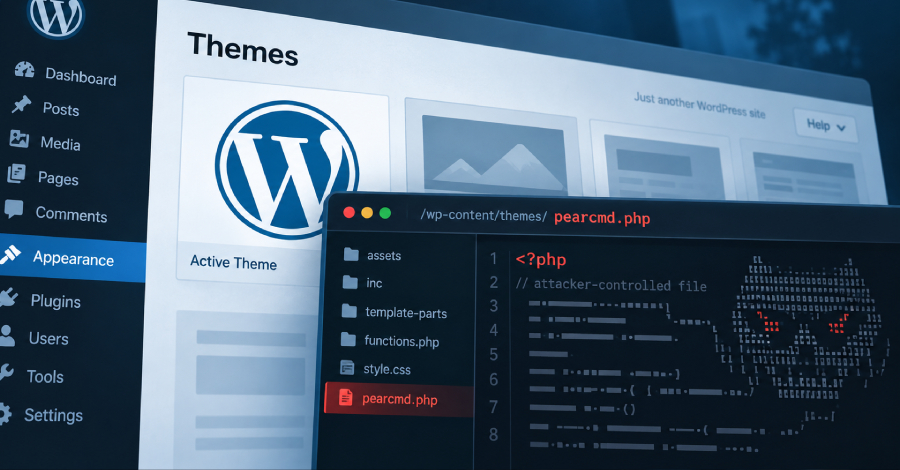
Threat actors have begun to actively exploit a critical security flaw in WordPress within hours of public disclosure.
The vulnerability in question is CVE-2026-87902 (CVSS score: 9.2), which could allow an unauthenticated attacker to obtain remote code execution (RCE).
“An unauthenticated attacker can make get_page_template() page-template resolution include a chosen readable local .php file…
Read the rest of the story at Read More
Source: The Hacker News


Leave a Comment