BlackX UEFI Bootkit Bypasses Secure Boot on Patched Windows Systems Missing Revocations

Diplomatic organizations in Central Asia have been targeted by a sophisticated new Unified Extensible Firmware Interface (UEFI) bootkit called BlackX. The activity, which singled out diplomatic entities in Tajikistan, Uzbekistan, and Turkmenistan in early 2026, is suspected to be orchestrated
Ruby Fixes Three Regex Engine Bugs Responsible for Four Critical GitLab RCE Flaws

Ruby has released versions 4.0.9, 3.4.12, and 3.3.13 to fix three bugs in Onigmo, the regular expression engine built into the language. The bugs lie behind four critical security flaws that GitLab patched over the past month. GitLab found that

Exposed Infrastructure Reveals How Ransomware Affiliates Used AI Agents to Execute Intrusions

Cybersecurity researchers have discovered an artificial intelligence (AI)-driven intrusion ecosystem run by affiliates of the INC and The Gentlemen ransomware groups. Central to the operation is an “Autonomous Red Team Kill Chain Framework” referred to as Phantom. The threat actor

Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials

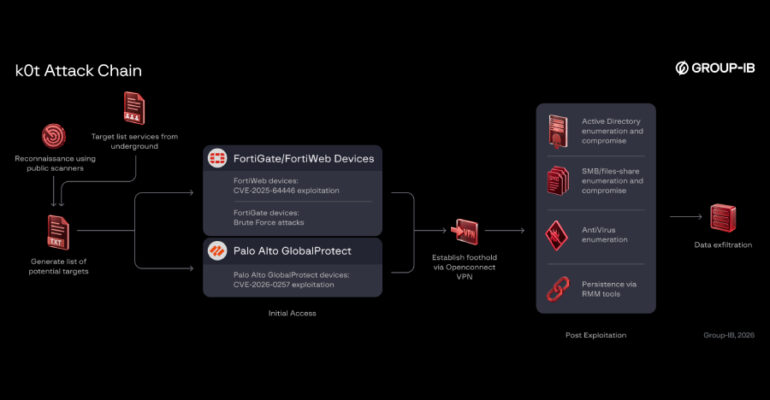
Cybersecurity researchers have disclosed details of a large-scale campaign that has targeted exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. “Artifacts from this investigation also indicate that operators in this campaign have obtained access

URGENT – PHP Warns of Another Unpatched RCE Two Days After Emergency PHP2Shell Patches

PHP has warned of another way an attacker could run code on a web server, two days after it shipped emergency fixes for the critical PHP2Shell flaws. The new issue, assigned CVE-2026-115560, affects only web applications configured in an unusual

Russian-Linked Hackers Used New Mesh Network Backdoor in Destructive Ukraine Attack

The Russian state-sponsored hacking group Sandworm teamed up with another threat actor to carry out a destructive wiping attack targeting a Ukrainian logistics company last year. According to ESET, the attack involved UAC-0099 (aka Earth Sirrush) obtaining initial access to

Critical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted Image

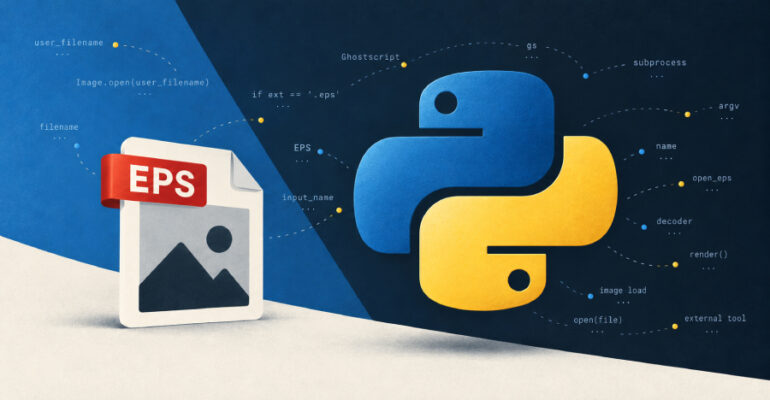
Pillow, the most widely used image library for Python, can be made to run operating system commands on a server by specifying the name of a file it is told to open. The flaw, CVE-2026-112900, is in the way Pillow handles

Critical x402 SDK Flaw Could Let Malicious APIs Drain AI Agents’ Token Balances

AI agents paying for API calls with the x402 SDKs could sign a payment for their full balance of a supported token if a malicious API asked for it, security firm V12 said on October 22. The cause was the SDKs’ default client, which

Researchers Demonstrate Node2Shell RCE Exploit on Node.js Build Using Crafted Brotli Data

Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated. Their “Node2Shell” proof of concept ran code on the official Node.js 24.22.0 image for Linux arm64, with no debugger

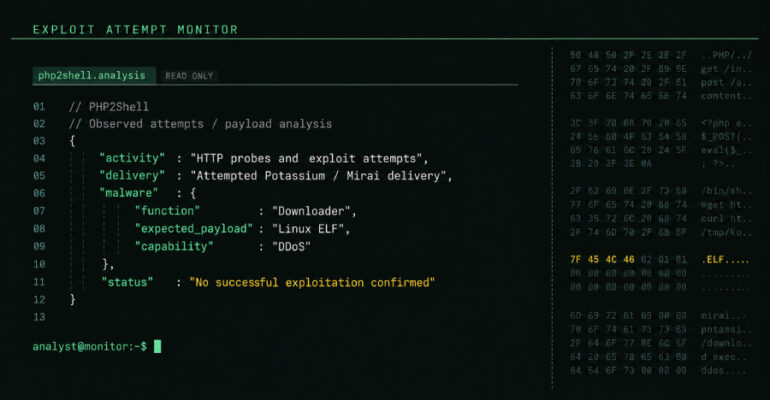
PHP2Shell Exploit Attempts Hit Millions as Attackers Try to Deploy Mirai Malware

Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant called Potassium, as it emerges that weaponizing the flaws may be harder than previously thought. The attacks