
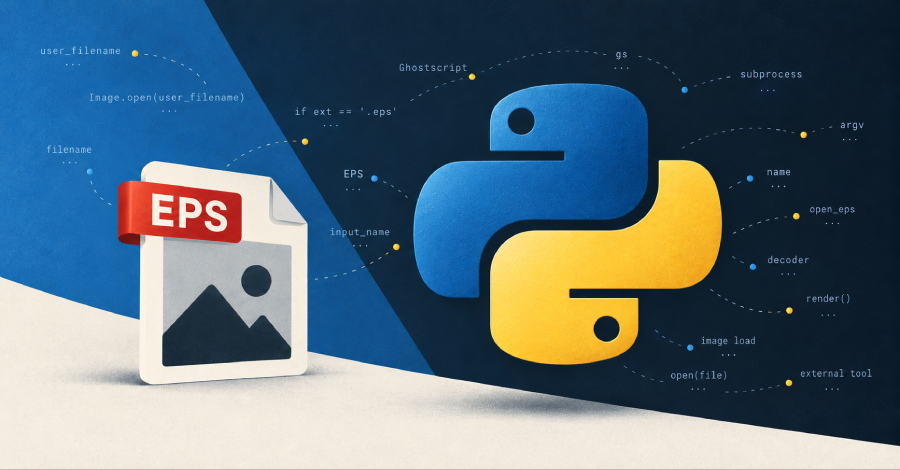
Pillow, the most widely used image library for Python, can be made to run operating system commands on a server by specifying the name of a file it is told to open.
The flaw, CVE-2026-112900, is in the way Pillow handles EPS images, which it opens by passing the file’s name to Ghostscript, a separate program it runs to turn the image into pixels, without checking the name first….
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment