Google Warns LLMjacking Attacks Are Costing Some Enterprises Up to $1 Million in Cloud Charges

Google on Monday warned that threat actors are hijacking enterprise access to Large Language Models (LLMs) to fraudulently leverage expensive computing resources and AI services. The tactic is called LLMjacking, a form of resource hijacking adapted for the LLM era,
cPGuard Update Channel Hijacked to Backdoor Linux Servers and Collect Password Hashes

An attacker broke into the update system of the cPGuard security tool on November 2 and used it to send a malicious script to customers’ Linux servers. The script installed a backdoor and collected password hashes and other sensitive files

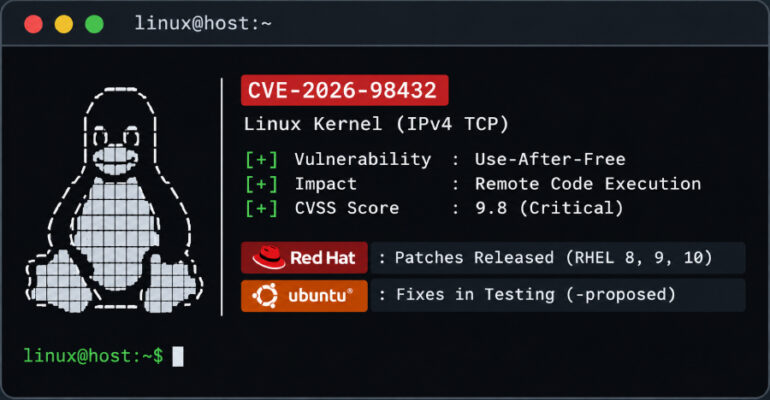
Red Hat Patches 9.8-Rated Linux TCP RCE Flaw While Ubuntu Releases Fixes for Testing

Fixed kernels for a use-after-free vulnerability in the Linux kernel’s IPv4 TCP code are now available for Red Hat Enterprise Linux 8, 9, and 10, while Ubuntu’s fixes for its three newest long-term-support releases remain in its opt-in testing channel with no

The 4 Elements of Exposure Prioritization and How to Operationalize Them

Your team is remediating more vulnerabilities than ever, yet your breach risk has barely changed. You’re spending too much time and effort on exposures attackers may never exploit, while higher-risk exposures sit, waiting in the queue. Gartner®’s report on exposure

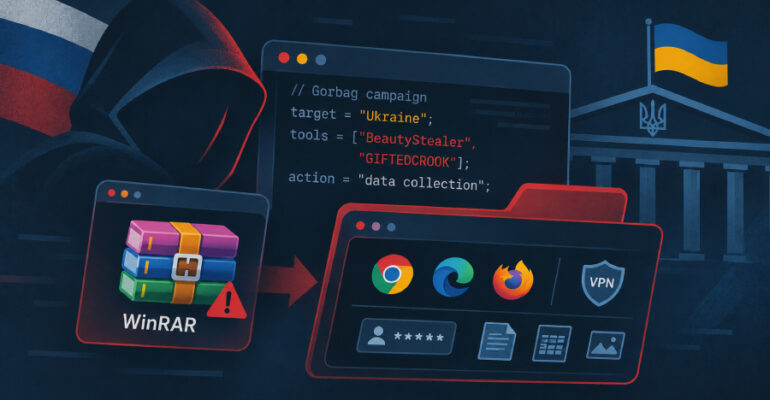
Russia-Aligned Gorbag Hackers Exploit WinRAR Flaw to Deploy Data-Stealing Malware

A Russia-aligned threat actor known as Gorbag has been observed using simple information stealer malware in attacks targeting Ukrainian organizations. “Active since at least February 2025, the group has focused exclusively on Ukrainian targets, with a clear preference for law

Hackers Exploit BTCPay Server Flaw to Steal Bitcoin and Litecoin From Hot Wallets

BTCPay Server, a self-hosted, open-source cryptocurrency payment processor, has urged users to install the latest version of its software in response to reports of Bitcoin and Litecoin being stolen from hot wallets on instances running older versions. “Our investigation found

Synology NAS Devices Targeted in Ransomware Attacks Exploiting Patched DSM Flaw

Synology is urging customers to update the DiskStation Manager (DSM) software powering its Network Attached Storage (NAS) devices following ransomware attacks. The Taiwanese vendor said it observed threat actors exploiting a vulnerability patched in December 2024 to target devices running

New Wave of Refrigeration Cyberattacks Hits Supermarkets Across Europe, Forcing Stores to Pull Food

Attackers remotely changed the settings on refrigeration controls at supermarkets in Belgium, Sweden, Estonia and other European countries overnight into Monday, November 2, warming fridges and freezers. No chain reported more than several dozen affected stores, and some had to

Attackers Exploit Critical Siemens IoT2050 Flaw to Plant Remote Command Backdoors

A maximum-severity security flaw impacting Siemens SIMATIC IoT2050 Advanced devices has come under active exploitation, VulnCheck has revealed. The vulnerability, tracked as CVE-2026-58115 (CVSS score: 10.0), is a case of missing authentication for a critical function that could be exploited

Attackers Target Unpatched CryptoPayment Gateway Flaw That Can Expose Wallet Credentials

Threat actors are attempting to exploit an unpatched maximum-severity security vulnerability in the CryptoPayment Gateway WordPress plugin, according to findings from Defused Cyber. The vulnerability in question is CVE-2026-81648, which carries a CVSS score of 10.0. Successful exploitation of the